


Bluetooth Hack Exposes 100M+ Audio Devices | Seller Security Alert
- Critical vulnerability affects wireless accessories across 10+ manufacturers






概览
The WhisperPair vulnerability represents a significant cybersecurity threat for cross-border e-commerce sellers in the wireless audio device market. Researchers from Belgium's KU Leuven University have uncovered a critical security flaw in Google's Fast Pair Bluetooth protocol that could compromise hundreds of millions of audio devices from major brands like Sony, JBL, Xiaomi, and Google.
Key operational implications for e-commerce sellers include immediate product security risks and potential brand reputation damage. The vulnerability allows hackers within 50 feet to:
- Hijack microphones in less than 15 seconds
- Disrupt audio streams
- Track user locations through compromised devices
- Bypass standard Bluetooth pairing security protocols
E-commerce platforms and sellers must take immediate action to mitigate risks. Manufacturers like Sony, JBL, and Xiaomi are rolling out firmware updates, but the responsibility falls on sellers to:
- Verify product firmware status
- Communicate security updates to customers
- Potentially recall or replace vulnerable inventory
- Update product listings with security information
The vulnerability highlights the critical need for rigorous security testing in connected device ecosystems. Cross-border sellers must now treat firmware updates as a core part of product lifecycle management, not just a peripheral concern. This incident underscores the importance of proactive security monitoring and rapid response mechanisms in the rapidly evolving wireless technology market.
问题 5
Which brands and devices are most impacted by the WhisperPair hack?
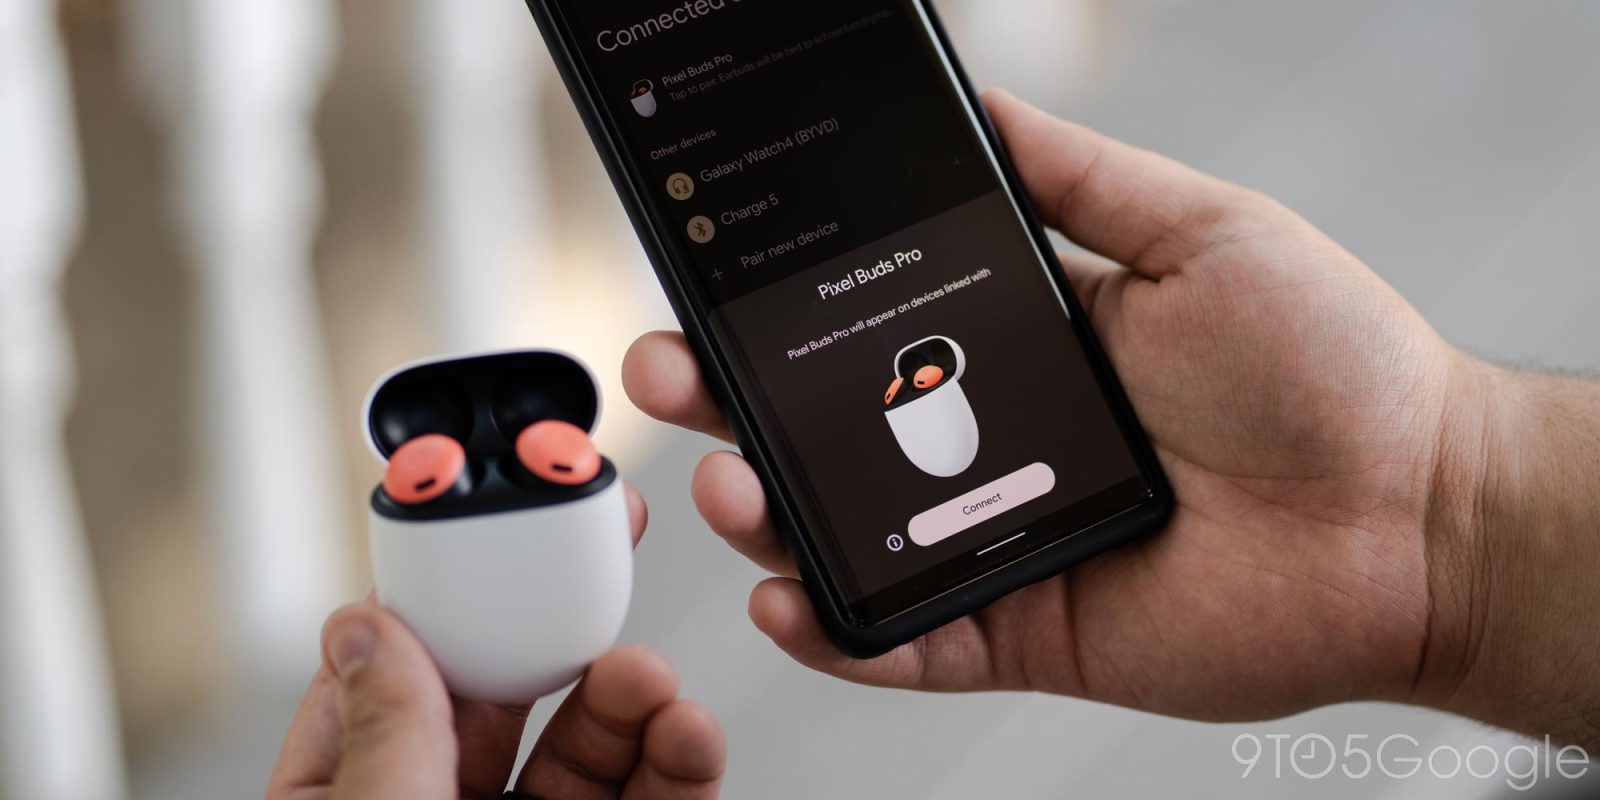
The vulnerability affects over 17 audio accessories from 10 manufacturers, including Sony, JBL, Xiaomi, Nothing, OnePlus, Jabra, and Google's Pixel Buds Pro 2. Devices using Google's Fast Pair protocol are particularly vulnerable to unauthorized access and tracking.
What immediate steps should e-commerce sellers take to protect their wireless device inventory?
Sellers should: 1) Contact manufacturers for firmware update details, 2) Pause sales of potentially vulnerable devices, 3) Update product listings with security information, 4) Prepare customer communication about potential risks and update procedures.