
AI Governance for Enterprise Teams: A Practical Starting Point
Summary
A practical enterprise AI governance guide covering foundational frameworks, risk tiering, model ownership, and operational processes. Targets engineering leaders and CTOs building governance from scratch. Key takeaways: start with an AI system inventory, assign named ownership, implement a minimum viable governance process (model registry, change gates, incident playbooks), and treat governance as an engineering discipline — not a compliance checkbox.
Details
 ALT: Enterprise team members building an AI governance framework for responsible, scalable AI deployment
Why AI Governance Has Become a Non-Negotiable for Enterprise Teams
Most engineering leaders first encounter AI governance the hard way — a model behaves unexpectedly in production, a sensitive customer dataset gets used in ways no one approved, or an audit surfaces a decision trail that simply doesn't exist. By that point, the damage is already done. The good news is that building a practical AI governance foundation does not require a dedicated compliance team or a multi-year transformation program to get started.
AI governance is the set of policies, processes, roles, and controls that ensure an organization's AI systems are developed, deployed, and maintained in ways that are accountable, transparent, and aligned with both business objectives and ethical standards. For enterprise teams in particular, governance is not a layer you bolt on after shipping — it is a structural decision that shapes everything from model selection to how you handle model drift in production.
This article lays out a practical starting point for enterprise teams who are past the "should we care about this?" phase and ready to ask "where do we actually begin?" We will cover the foundational concepts, common failure patterns, a step-by-step entry approach, and the comparisons that help you decide how to operationalize governance for your specific context.
Who This Guide Is For and Where It Applies
Applicable Scenarios:
- Enterprise teams that have deployed, or are actively building, AI-powered features or decision systems in production
- Engineering leaders and CTOs who need to establish accountability structures before regulatory pressure arrives
- Product teams integrating third-party AI models or large language models (LLMs) into customer-facing workflows
- Organizations operating in regulated industries — finance, healthcare, legal, HR — where model decisions carry legal or reputational consequences
Not Applicable or Use With Caution:
- Early-stage exploratory prototypes where the AI system has no production exposure and no real-user data — lightweight oversight is still wise, but a full governance program may be premature overhead
- Teams that already operate under a mature, audited AI risk framework; this guide targets teams building that foundation, not those refining an existing mature program
The Governance Gap That Catches Most Teams Off Guard
Enterprise adoption of AI has outpaced the development of internal controls to manage it responsibly. This is not a failure of intent — it is a structural lag. Teams move fast to demonstrate value, models get promoted to production, and governance conversations get deferred to "a later sprint." A pattern that appears consistently in engineering advisory work is that by the time a team recognizes the governance gap, they are already managing several live AI systems with no documented ownership, no model versioning policy, and no defined process for handling bias complaints or model rollback.
According to Collibra, a recognized authority in enterprise data intelligence, organizations that approach AI governance reactively — after a compliance incident or public failure — face substantially higher remediation costs and organizational trust deficits compared to those that establish controls proactively. The challenge is real: AI systems introduce novel risk categories that traditional IT governance frameworks were not designed to address. Model behavior can degrade silently over time due to data drift. Outputs can be statistically biased in ways that standard QA testing does not catch. The chain of responsibility for a model's decision can be genuinely ambiguous across data science, product, and engineering teams.
The emergence of regulatory frameworks — including the EU AI Act and sector-specific guidance from bodies like the National Institute of Standards and Technology (NIST) with its AI Risk Management Framework — has further raised the stakes. These are not hypothetical future requirements. They are shaping enterprise procurement decisions, partner agreements, and, in regulated sectors, legal liability today.
For teams asking where to begin, the answer is to start with the three layers that matter most in the near term: clarity of ownership, visibility into what you are running, and a defined process for handling failures. If you are also evaluating the broader infrastructure context, understanding how to think about build vs. buy decisions for AI infrastructure is a natural companion conversation to governance design — the architectural choices you make directly constrain what governance controls are even possible.
Building an AI Governance Foundation: A Practical Framework
Three-Step Quick Start
Step 1: Inventory Your Current AI Surface Area
Before you can govern AI systems, you need to know what you are actually running. This sounds obvious, yet in a pattern seen repeatedly across advisory engagements, teams routinely undercount their AI surface area by a significant margin. An honest inventory covers not just custom-built models, but every third-party AI API, embedded model in a SaaS tool, and automated decision component in your stack. For each system, document: what decision or output it produces, what data it consumes, who owns it, and whether it has any downstream effect on customers or employees. This exercise alone surfaces ownership gaps that no governance policy can fix until they are acknowledged.
Step 2: Assign Ownership and Define Accountability Tiers
Every AI system in production needs a named owner — a human being who is accountable for its behavior, its performance, and the response when something goes wrong. This is not the same as the engineer who built it. Ownership is a function of ongoing accountability, which means it belongs to a role, not just a person. Once ownership is assigned, tier your systems by risk level. A content recommendation engine carries different risk than an automated credit-scoring model or an HR screening tool. Higher-risk tiers require more rigorous controls: documented model cards, bias audits, mandatory human review thresholds, and defined escalation paths.
Step 3: Establish a Minimum Viable Governance Process
A minimum viable governance process for most enterprise teams includes four components: a model registry (a central record of what is deployed, what version, trained on what data), a change management gate (no model update goes to production without a documented review), an incident response playbook (what happens when a model misbehaves, including rollback procedures), and a regular review cadence (at minimum quarterly for high-risk systems). This does not require specialized governance software on day one. A well-structured internal wiki and a consistent review meeting is a legitimate starting point. The discipline matters more than the tooling in the early stages.
AI Governance Approach Comparison
Enterprise teams typically face a choice among three operational approaches to standing up governance. The right fit depends on organizational maturity, regulatory exposure, and available internal expertise.
Introductory note: the table below compares the three most common governance implementation approaches. No single approach is universally superior — the optimal choice depends on your team's current maturity and risk profile.
| Comparison Dimension | Centralized Governance Team | Federated Model (Embedded) | Hybrid Approach |
|---|---|---|---|
| Ownership clarity | High — single team owns the framework | Moderate — ownership distributed by product team | High — central policy, local execution |
| Speed to implement | Slower — requires hiring or reassignment | Faster — leverages existing team structure | Moderate — policy-first, then local rollout |
| Scalability across products | Moderate — bottleneck risk as AI expands | High — scales naturally with product growth | High — designed for scale from the start |
| Consistency of controls | High — uniform standards enforced centrally | Variable — depends on team discipline | High — central standards with local flexibility |
| Regulatory audit readiness | High — centralized documentation and evidence | Lower — requires coordination across teams | High — if central registry is well-maintained |
| Best suited for | Heavily regulated industries, large orgs | Fast-moving product orgs, lower regulatory exposure | Organizations scaling AI across multiple domains |
Making Governance Operational Without Killing Engineering Velocity
The most common objection to enterprise AI governance is that it slows teams down. This is a legitimate risk if governance is designed as a gatekeeping function rather than an enabling one. The goal should be to make the right behavior the default behavior, not to add approval queues that engineers route around.
Model cards as living documentation. A model card is a short, structured document that captures the essential facts about an AI model: its intended use, its training data sources, known limitations, and performance metrics across relevant demographic or contextual subgroups. According to read.ai's practical guidance on AI governance, model cards are among the most effective lightweight mechanisms for creating accountability without requiring heavy process overhead. They force the team building the model to make explicit what is often left implicit, and they give downstream teams the context they need to use the model appropriately.
Risk tiering reduces friction for low-stakes systems. Not every AI feature carries the same risk. A grammar suggestion tool and an automated loan decision engine should not go through the same review process. Risk tiering — assigning systems to low, medium, or high risk categories based on their potential for harm, reversibility of decisions, and data sensitivity — allows governance controls to scale proportionally. Low-risk systems get lightweight documentation and a self-service review checklist. High-risk systems get mandatory human review, bias auditing, and regular third-party or internal red-teaming.
Incident response planning closes the accountability loop. According to guidance from adaptive security practitioners in enterprise AI risk management, one of the most overlooked governance gaps is the absence of a defined incident response process for AI-specific failures. Traditional incident response processes handle system outages and security breaches, but they are generally not designed to handle cases like model bias surfacing in production, a model generating harmful outputs at scale, or a data pipeline poisoning a live model's inputs. An AI-specific incident playbook should define: what triggers an incident declaration, who is notified and in what order, how a rollback or override is initiated, how affected parties are communicated with, and what post-incident review is required before the system is restored.
Audit trails are not optional in regulated environments. If your AI system is making or materially influencing decisions in a regulated domain — credit, employment, healthcare, legal — you are almost certainly subject to explainability and audit requirements, whether or not your legal team has formalized that assessment yet. Designing for auditability from the start means logging inputs, outputs, and model versions in a queryable format, and ensuring that a human reviewer can reconstruct why a particular decision was made. This is an architectural decision as much as a governance one. If you are uncertain how to structure AI systems for auditability from the ground up, exploring what an AI architecture engagement actually covers in practice is a useful starting reference.
Bias and fairness monitoring requires ongoing attention. Model performance on fairness dimensions does not remain static after deployment. Data distributions shift, user behavior changes, and edge cases accumulate. A governance framework that only evaluates fairness at training time will consistently miss the drift that occurs in production. High-risk systems should have automated monitoring for fairness-relevant metrics, with defined thresholds that trigger human review when crossed. For teams building machine learning pipelines that need to sustain this kind of monitoring at scale, the engineering patterns involved in building ML pipelines that scale past the prototype stage are directly applicable.
Advanced Considerations: Edge Cases and Persistent Misconceptions
Governing AI you do not own. A significant and growing portion of enterprise AI exposure comes not from internally built models but from third-party AI services — LLM APIs, embedded AI features in SaaS platforms, AI-assisted tools used by employees. The governance challenge here is that you do not control the model, but you are still accountable for the outputs it produces in your context. Practical controls include: contractual provisions requiring vendor transparency about model changes, internal policies on what data can be sent to external AI services, and output-level monitoring for behavior that violates your standards regardless of source.
Misconception: governance is a compliance function, not an engineering function. One of the most damaging framings in enterprise AI governance is treating it as a task for the legal or compliance team to own. Governance is deeply technical. Decisions about model versioning, logging architecture, rollback mechanisms, bias monitoring pipelines, and explainability tooling are all engineering decisions that have governance implications. The most effective governance programs are co-designed by engineering leadership and policy stakeholders — not handed off from one to the other.
Misconception: a governance framework can be purchased off the shelf. Governance tooling is useful, but no vendor tool substitutes for the foundational work of defining ownership, establishing risk tiers, and building the cultural expectation that AI systems require ongoing stewardship. Teams that invest in tooling before completing the foundational work typically end up with sophisticated software that nobody is using consistently.
The role of the NIST AI Risk Management Framework. The AI Risk Management Framework, published by the National Institute of Standards and Technology, is currently the most actionable voluntary standard available to enterprise teams in the United States for structuring AI risk management programs. It organizes AI risk management across four core functions — Govern, Map, Measure, and Manage — and is designed to be adaptable to organizations of varying sizes and risk profiles. Referencing this framework when building internal governance documentation adds credibility and creates alignment with the direction regulatory expectations are moving.
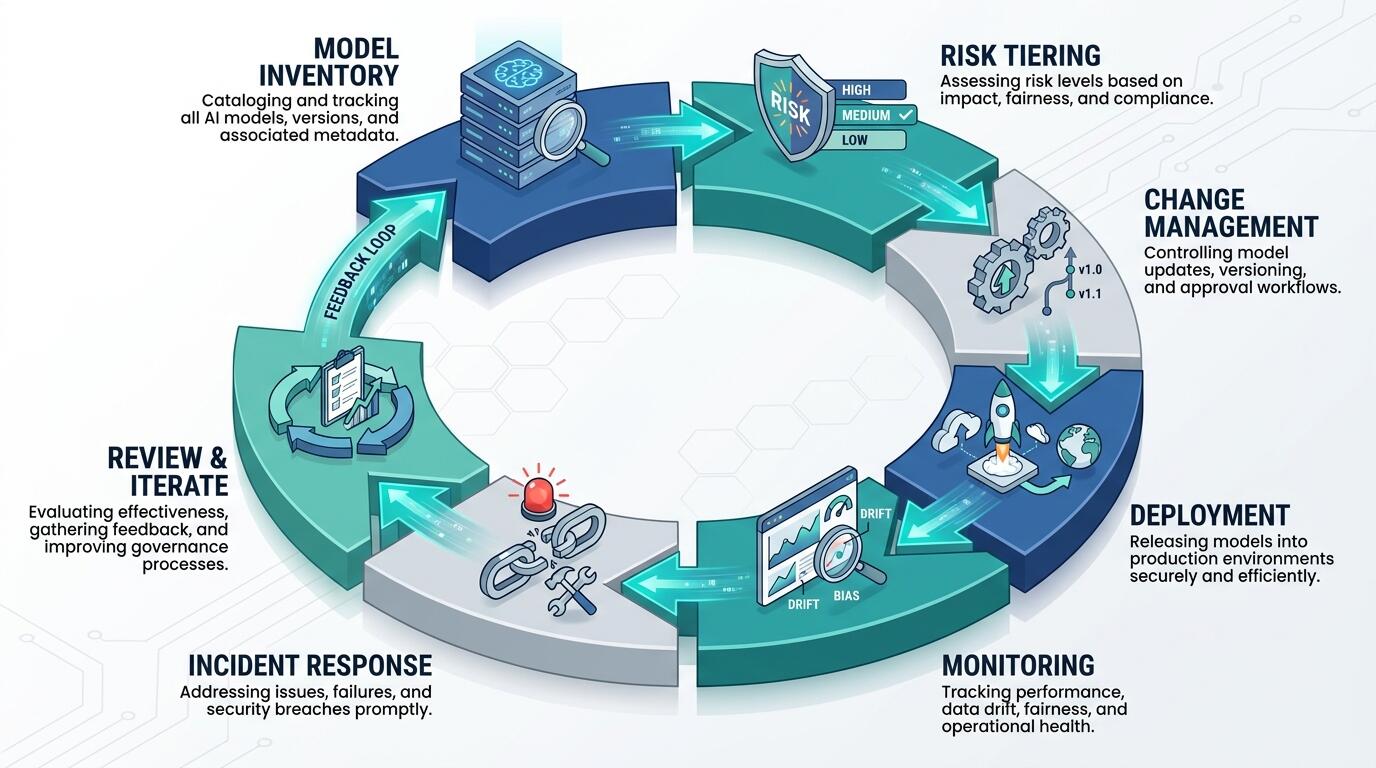 ALT: Diagram illustrating an enterprise AI governance lifecycle from model inventory and risk tiering to ongoing monitoring and incident response
People Also Ask
Q1: How should enterprise teams prioritize which AI systems to govern first?
Prioritization should follow risk exposure, not deployment order. Start with AI systems that make or materially influence consequential decisions — credit approvals, hiring screens, patient triage, fraud determinations — because these carry the highest regulatory and reputational risk. Next, prioritize systems with large user-facing scale, since behavioral failures reach more people faster. Systems with clear data sensitivity concerns (personal data, protected categories) also move up the priority queue regardless of the nature of the decision they support. Low-risk, internal-only tools with easily reversible outputs can be governed with lighter controls.
Q2: Is AI governance only relevant for large enterprises, or do mid-market and scaling startups need it too?
AI governance is relevant at any scale where AI systems are making real decisions that affect real people. Scaling startups often assume governance is a "large enterprise problem," but the window between "fast-growing startup" and "regulatory enforcement target" is shrinking, particularly in regulated industries. The practical argument for early-stage governance is also cost-based: retrofitting accountability, logging, and explainability into systems that were not designed for it is substantially more expensive and disruptive than building with governance principles from the start. The framework should be proportionate to the risk profile, not the headcount.
Q3: How long does it typically take to implement a foundational AI governance program?
The foundational layer — inventory, ownership assignment, risk tiering, and a minimum viable governance process — can be stood up within a matter of weeks for a focused team with executive support. Mature governance, including bias monitoring pipelines, audit-ready logging infrastructure, and a functioning model registry, is a multi-month effort that scales with the number and complexity of systems in scope. The most important accelerant is organizational commitment at the leadership level; governance programs that lack executive sponsorship tend to stall at the documentation stage and never achieve operational traction.
Summary
AI governance for enterprise teams is not a compliance checkbox — it is an engineering discipline that determines whether your AI systems remain trustworthy, auditable, and aligned with your organization's intent as they scale and evolve in production.
Key Takeaways:
- Start with an honest inventory of every AI system in production, including third-party and embedded AI components, before designing any governance controls.
- Assign named ownership and tier systems by risk level — governance controls should be proportionate to the consequences of failure, not uniform across all AI use cases.
- A minimum viable governance program covers a model registry, a change management gate, an incident response playbook, and a regular review cadence — tooling is secondary to these fundamentals.
- Audit trails, model cards, and fairness monitoring are not optional in regulated domains; they are architectural decisions that must be made at design time, not retrofitted later.
- Governance that slows engineering down is governance that has been designed incorrectly — the goal is to make responsible behavior the default, not to add process friction.
The next step for most teams is the inventory: carve out structured time with your engineering leads to map what you are actually running, who owns it, and what decisions it is making. That exercise alone will make the path forward clear.
If your team is navigating the architectural and organizational decisions that come with building AI systems responsibly at scale, visit the Darius website to explore shipped projects and learn how engineering leadership and AI architecture expertise can help you build systems that are not just functional, but genuinely production-ready.
Sources & Citations
- Collibra. "A practical guide to governing AI at enterprise scale".
- read.ai. "What Is AI Governance? A Practical Guide for Teams".
https://www.read.ai/articles/what-is-ai-governance-a-practical-guide-for-teams
- Adaptive Security. "AI Governance Best Practices: Guide for Enterprise Leaders".
- National Institute of Standards and Technology (NIST). AI Risk Management Framework.
Note: Standards and regulatory frameworks may be updated; please consult the latest official documentation or qualified advisors to verify current requirements.