
Governing AI Systems as You Approach 2027: What Enterprise Teams Are Doing Now
Summary
This article outlines 9 actionable AI governance practices for enterprise engineering teams ahead of 2027 regulatory changes. Targeting CTOs, engineering managers, and founders, it argues governance must be an embedded engineering discipline—not a compliance checkbox. Key takeaways: build AI inventories, apply risk tiering, enforce human oversight, and extend governance to vendors.
Details
 ALT: Enterprise teams governing AI systems with frameworks, policies, and oversight strategies approaching 2027
What Forward-Looking Enterprise Teams Are Doing Now to Govern AI Systems Before 2027
AI governance is no longer a compliance checkbox — it is an active engineering and organizational discipline that separates enterprises building durable AI systems from those scrambling to retrofit controls after incidents occur. As regulatory pressure intensifies globally and AI systems grow more deeply embedded in critical workflows, enterprise teams that get governance right early are gaining a structural advantage that is increasingly difficult to close.
This article distills the concrete practices we consistently see leading engineering organizations adopt as they move toward production-grade, governed AI at scale. The items here are drawn from practitioner experience across AI architecture engagements, systems design work, and the hard lessons learned when governance is treated as an afterthought. Whether you are a CTO defining your AI strategy, an engineering manager inheriting a patchwork of models and pipelines, or a founder thinking about what responsible AI deployment actually looks like in practice — this list is designed to give you a map of where the serious teams are investing right now, and why each decision matters.
The practices below were selected based on one criterion: they are observable, actionable patterns that address real failure modes in enterprise AI systems — not aspirational frameworks that look good in a slide deck but dissolve on contact with production environments.
The Governance Practices Enterprise AI Teams Are Prioritizing Now
Establishing a Centralized AI Inventory Before Anything Else
Governing AI systems requires knowing what AI systems you actually have. This sounds obvious, yet a pattern we consistently see in early-stage and mid-growth organizations is that AI assets are scattered — models embedded in product features, automation scripts running in data pipelines, third-party model APIs consumed across teams without central visibility.
An AI inventory is a structured registry that captures every model in production, its purpose, its data dependencies, who owns it, how it makes decisions, and what its risk classification is. Without this registry, governance is theater. You cannot audit what you cannot enumerate.
Best for: Any organization that has moved beyond a single-model prototype into a landscape of multiple AI touchpoints across products or internal tooling.
Watch out: Inventories go stale fast. A registry with no ownership model becomes a liability in itself — build the maintenance process before you build the spreadsheet.
Defining Risk Tiering for AI Use Cases
Not every AI system carries the same risk profile, and treating them all identically is a resource misallocation that blunts your governance program. Risk tiering is the practice of classifying AI use cases along dimensions such as decision consequence, reversibility of outcomes, regulatory exposure, and affected population.
According to guidance from the National Institute of Standards and Technology (NIST) — specifically their AI Risk Management Framework — organizations benefit from a structured approach that maps AI system characteristics to risk categories, enabling proportionate controls rather than blanket restrictions. In our work with clients, translating this into a practical tiering matrix (typically three to four tiers) is one of the highest-leverage early governance investments an enterprise team can make.
Best for: Teams that need to prioritize governance investment across a portfolio of AI systems and avoid over-engineering controls for low-stakes use cases.
Watch out: Tier assignments should be revisited as use cases evolve. A model originally scoped for internal reporting can drift into higher-stakes territory as business processes change around it.
Implementing Model Cards and System Documentation as Living Artifacts
Model cards — structured documentation that describes a model's intended use, training data characteristics, evaluation results, and known limitations — are becoming a baseline expectation in enterprise AI governance. The concept, formalized in academic literature and adopted by major AI research organizations, is now being operationalized at the system level by engineering teams that want audit-ready documentation without bureaucratic overhead.
In practice, the teams doing this well treat model cards not as one-time outputs but as living artifacts tied to the model's lifecycle. Every significant update to training data, fine-tuning approach, or deployment scope triggers a documentation review. This creates a traceable history that satisfies both internal governance requirements and increasingly demanding external audit processes.
Best for: Organizations operating in regulated industries or those anticipating regulatory scrutiny, and any team deploying models that influence consequential decisions.
Watch out: Documentation without a clear owner becomes shelfware. Assign explicit documentation ownership within your ML or platform engineering team, not to a governance committee that meets quarterly.
Building Observability Into AI Systems at the Architecture Level
AI observability is the practice of instrumenting AI systems — including models, pipelines, and their integration points — to surface behavioral drift, data quality degradation, output distribution shifts, and latency anomalies in real time. This is distinct from standard application monitoring, which typically measures infrastructure health rather than model behavior.
A pattern we consistently see in mature AI engineering organizations is that observability is designed in from the start, not bolted on after a production incident. This means defining what "normal" looks like at inference time, establishing baselines for output distributions, and building alerting that triggers on behavioral anomalies rather than just system errors. If you are thinking about how to build machine learning pipelines that scale past the prototype stage, observability architecture is one of the first decisions that separates systems that hold up in production from those that quietly degrade.
Best for: Any team running models in production where behavioral drift has real consequences — recommendation systems, fraud detection, customer-facing AI features.
Watch out: Observability tooling generates significant data. Without clear runbooks for what to do when an alert fires, teams accumulate dashboards that no one acts on.
Formalizing Human-in-the-Loop Requirements by Decision Type
Human oversight of AI decisions is not a binary choice — it exists on a spectrum from full automation to mandatory human review, and the right position on that spectrum depends on the stakes, reversibility, and regulatory requirements of each decision type. Enterprise teams approaching 2027 are moving away from ad hoc oversight practices toward formalized policies that specify, by decision category, when human review is required, what that review must entail, and how override decisions are logged.
The European Union's AI Act — a regulatory framework establishing risk-based requirements for AI systems deployed in the EU — explicitly mandates human oversight provisions for high-risk AI systems. Even for organizations not directly subject to the EU AI Act, its framework is influencing governance expectations globally, and engineering teams that design with human oversight as a first-class system requirement are better positioned for compliance regardless of jurisdiction.
Best for: Organizations deploying AI in hiring, credit, healthcare, legal, or any other domain where automated decisions carry regulatory or ethical exposure.
Watch out: "Human in the loop" is meaningless if the human has insufficient context, time, or authority to meaningfully review the AI's output. Design the review interface and process with the same rigor as the model itself.
Instituting Adversarial Testing and Red-Teaming Before Production
Adversarial testing — deliberately attempting to cause an AI system to fail, produce harmful outputs, or behave unexpectedly — is one of the most underused governance practices in enterprise AI programs. Red-teaming, adapted from cybersecurity practice, applies a structured adversarial lens to AI system behavior across dimensions including safety, fairness, robustness, and security.
In our work with clients building production AI systems, we find that adversarial testing surfaces failure modes that neither unit tests nor standard evaluation benchmarks catch. This includes prompt injection vulnerabilities in LLM-based systems, distributional edge cases that cause model outputs to degrade unpredictably, and interaction patterns that expose unintended system behaviors. Per guidance from the U.S. Cybersecurity and Infrastructure Security Agency (CISA), organizations deploying AI systems should incorporate adversarial testing as a standard component of pre-deployment validation.
Best for: Teams deploying LLM-based features, any AI system that processes user-generated input, and high-stakes decision systems where unexpected model behavior has serious downstream consequences.
Watch out: Adversarial testing is not a one-time gate. As models are updated and deployment contexts evolve, the adversarial surface changes. Build red-teaming into your regular release process, not just your initial launch.
Establishing Data Lineage and Consent Tracking for Training and Inference
Data governance is inseparable from AI governance. Enterprise teams that lack clear data lineage — the documented trail of where training data came from, how it was processed, what consent was obtained, and how it flows through the system — are exposed to both regulatory risk and operational fragility. When a data quality issue surfaces in production, teams without lineage documentation face an expensive and time-consuming incident response that could have been structured in advance.
Modern data lineage practices in AI contexts extend beyond training data to include inference-time data — particularly relevant for systems that consume personal data in real time. Organizations evaluating their data infrastructure as part of an AI architecture engagement should treat lineage tooling as a governance dependency, not an optional enhancement.
Best for: Any organization handling personal data, operating in regulated industries, or building AI systems where training data provenance may be subject to legal challenge.
Watch out: Lineage tooling adds pipeline complexity. Invest in lineage proportionate to your actual risk exposure — high-stakes, regulated use cases warrant comprehensive lineage; low-risk internal tooling may warrant lighter-weight tracking.
Creating a Governance-Aware AI Procurement and Vendor Assessment Process
A significant proportion of enterprise AI capability today is sourced from third-party vendors and foundation model providers. This means that a substantial portion of your AI governance exposure lives outside your direct engineering control. Enterprise teams approaching 2027 are formalizing AI-specific procurement criteria that assess vendors across dimensions including model transparency, data handling practices, incident response processes, and alignment with emerging regulatory requirements.
When you are assessing what to build versus buy for your AI infrastructure, governance considerations should be weighted explicitly alongside capability and cost. A vendor's inability to answer basic questions about their model's training data provenance, their security posture for inference-time data, or their policy on model versioning and deprecation is a governance signal, not just a commercial inconvenience.
Best for: Organizations that rely on external model APIs, AI SaaS platforms, or third-party AI components embedded in their product stack.
Watch out: Vendor assessments conducted only at procurement time create a false sense of security. AI vendor practices evolve — build periodic reassessment into your vendor management program.
Embedding Governance Accountability Into Engineering Team Structures
Governance frameworks without organizational accountability fail reliably. The most effective AI governance programs we see are those where accountability is embedded in engineering team structures — not delegated entirely to a separate governance function that operates at arm's length from the engineers building and deploying systems.
This means designated AI system owners who are responsible for a model's behavior in production, clear escalation paths for governance exceptions, and governance requirements included in engineering definitions of done. The goal is to make governance a property of how your engineering team works, not an external audit process that happens to your team. Understanding what a structured AI architecture engagement looks like can help leadership teams understand how governance responsibilities should be embedded from the earliest stages of system design.
Best for: Organizations moving from ad hoc AI experimentation to systematic AI deployment at scale, and any team where governance has historically been siloed in legal or compliance functions.
Watch out: Embedding accountability requires clarity about authority. Engineers cannot be accountable for governance outcomes they lack the authority to act on — ensure team structure and decision-making authority are aligned.
Quick Comparison at a Glance
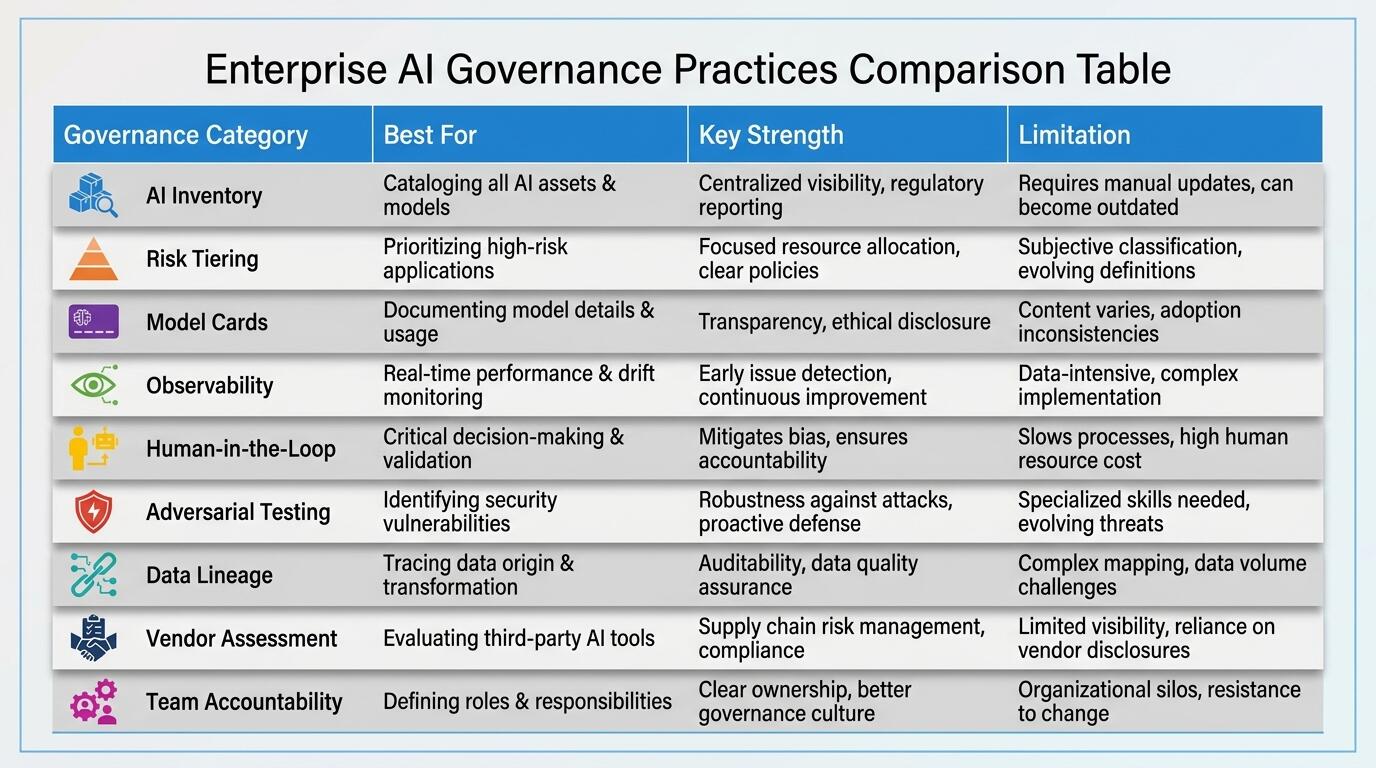 ALT: Comparison table of enterprise AI governance practices for teams preparing AI systems ahead of 2027 regulatory landscape
| Governance Practice | Best For | Key Strength | Limitation |
|---|---|---|---|
| Centralized AI Inventory | Any multi-model organization | Complete visibility across AI assets | Requires continuous maintenance |
| Risk Tiering | Portfolio-level prioritization | Proportionate, efficient governance | Tier assignments can drift with use case evolution |
| Model Cards and System Documentation | Regulated industries, audit-ready teams | Traceable, auditable model history | Requires clear ownership to stay current |
| AI Observability at Architecture Level | Production model operators | Real-time behavioral insight | Generates noise without actionable runbooks |
| Human-in-the-Loop Policies | High-stakes or regulated decisions | Regulatory alignment, error containment | Ineffective without proper review context and authority |
| Adversarial Testing and Red-Teaming | LLM deployments, high-stakes systems | Surfaces hidden failure modes | Must be repeated; surface changes over time |
| Data Lineage and Consent Tracking | Personal data, regulated contexts | Risk exposure reduction, incident response speed | Adds pipeline complexity |
| Governance-Aware Vendor Assessment | External AI API and SaaS consumers | Extends governance beyond internal systems | Point-in-time assessments create false security |
| Embedded Team Accountability | Scaling AI organizations | Governance as engineering culture | Requires aligned authority, not just responsibility |
How to Choose the Right Governance Practices for Your Organization
The most common misconception about AI governance is that it requires a comprehensive, fully formed program to be valuable. In reality, a targeted investment in two or three of the practices above — applied to your highest-risk AI systems — delivers substantially more governance value than a broad, shallow program applied uniformly across everything.
The right starting point depends on where your organization sits in its AI maturity curve and what your most pressing exposure is.
If you are operating multiple AI systems without a clear inventory of what they are and who owns them, start with the AI inventory and risk tiering. These are foundational — every other governance practice depends on knowing what you have and how consequential it is.
If you are deploying AI in a regulated industry or in decisions that directly affect individuals — hiring, lending, healthcare, legal — prioritize human-in-the-loop policies and data lineage. These are where regulatory and legal exposure is most immediate.
If you are heavily reliant on third-party model APIs and AI platforms, the vendor assessment process is your most urgent gap. Your governance exposure is only as strong as your weakest vendor's practices.
If you are running LLM-based features that process user-generated input, adversarial testing and AI observability should be considered non-negotiable pre-deployment requirements.
For organizations that have reached a meaningful scale of AI deployment and are concerned about sustainable governance over time, embedding accountability in engineering team structures is the practice with the longest-term leverage. Technical controls degrade when organizational accountability is absent — the inverse is also true.
A practical note: governance practices compound. An organization with a solid inventory, clear risk tiers, and embedded team accountability will implement observability, documentation, and testing practices more effectively because the foundation is sound. Sequence your investments accordingly.
Frequently Asked Questions FAQ
Q1: How should enterprise teams prioritize AI governance when resources are constrained?
Effective AI governance under resource constraints starts with ruthless prioritization by risk, not by breadth. Identify your two or three AI systems with the highest consequence profiles — those influencing significant decisions, handling sensitive data, or carrying regulatory exposure — and apply structured governance specifically there. A tight, well-executed governance program on high-risk systems delivers more organizational protection than a light-touch program applied uniformly. Build governance depth before governance width.
Q2: Are AI governance frameworks like NIST AI RMF or the EU AI Act directly applicable to all organizations?
The NIST AI Risk Management Framework is voluntary guidance designed for broad applicability — any organization can adopt its principles regardless of jurisdiction or industry. The EU AI Act has specific jurisdictional scope, applying to AI systems deployed in the EU or affecting EU residents. However, both frameworks are shaping global governance expectations, and many organizations outside the EU are aligning their practices to EU AI Act risk categories as a forward-looking standard, even where direct legal obligation does not yet apply.
Q3: How long does it typically take to stand up a foundational AI governance program?
A foundational program — covering an AI inventory, risk tiering, and basic model documentation for a defined set of in-scope systems — can be established in weeks rather than months when leadership is aligned and scope is bounded. The more complex phases, such as embedding observability infrastructure, formalizing human-oversight workflows, and integrating governance into engineering team structures, unfold over quarters. Starting narrow and expanding iteratively is consistently more effective than planning a comprehensive program that takes too long to deliver initial value.
Key Takeaways
AI governance is an engineering discipline, not a compliance formality — teams that embed governance practices into their architecture and team structures build more durable, auditable, and resilient systems.
A centralized AI inventory and risk-based tiering are foundational prerequisites; no other governance practice delivers its full value without them.
Human oversight requirements, data lineage, and adversarial testing are the three highest-leverage practices for organizations with regulated or high-stakes AI use cases.
Vendor governance is a gap most enterprise teams underestimate — your AI governance exposure extends to every third-party model and platform your systems depend on.
Governance accountability must live in engineering team structures, not only in governance committees. Authority and responsibility need to be aligned for accountability to be real.
As the regulatory and operational environment for AI systems continues to evolve, the organizations that are investing in governance now — not reactively, but as a deliberate engineering and organizational strategy — are building the capability to move faster and with greater confidence than those that defer the work.
Ready to build AI systems with governance designed in from the start? Visit the Darius website to explore shipped projects, architecture thinking, and how a practitioner-first approach to AI engineering can help your team build smarter, more responsible systems — from initial architecture design through to live production deployment.
References
- National Institute of Standards and Technology (NIST). "AI Risk Management Framework (AI RMF)".
- European Parliament and Council of the European Union. "Artificial Intelligence Act (EU AI Act)".
https://www.europarl.europa.eu/
- U.S. Cybersecurity and Infrastructure Security Agency (CISA). "Guidance on Secure AI Development and Deployment".
Note: Standards and regulatory frameworks may be updated; please check the latest official documents or consult professional advisors.