


Microsoft Security Patches February 2026 | Critical Impact for E-Commerce Infrastructure
- 59 vulnerabilities patched including 6 actively exploited zero-days affecting Windows, Office, and Remote Desktop; federal agencies mandated to patch by March 3, 2026; e-commerce sellers relying on Windows infrastructure face operational risk and compliance urgency



















Overview
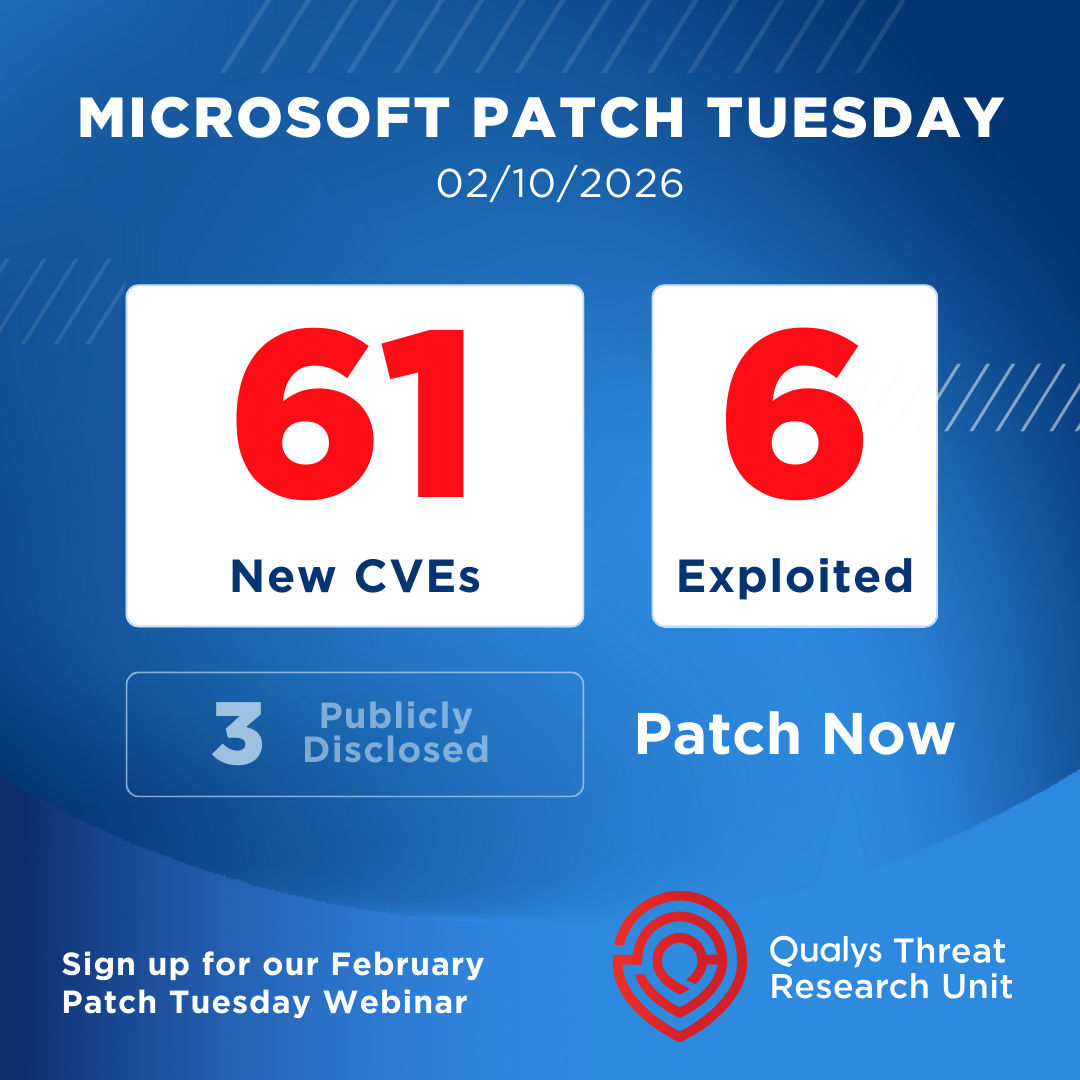
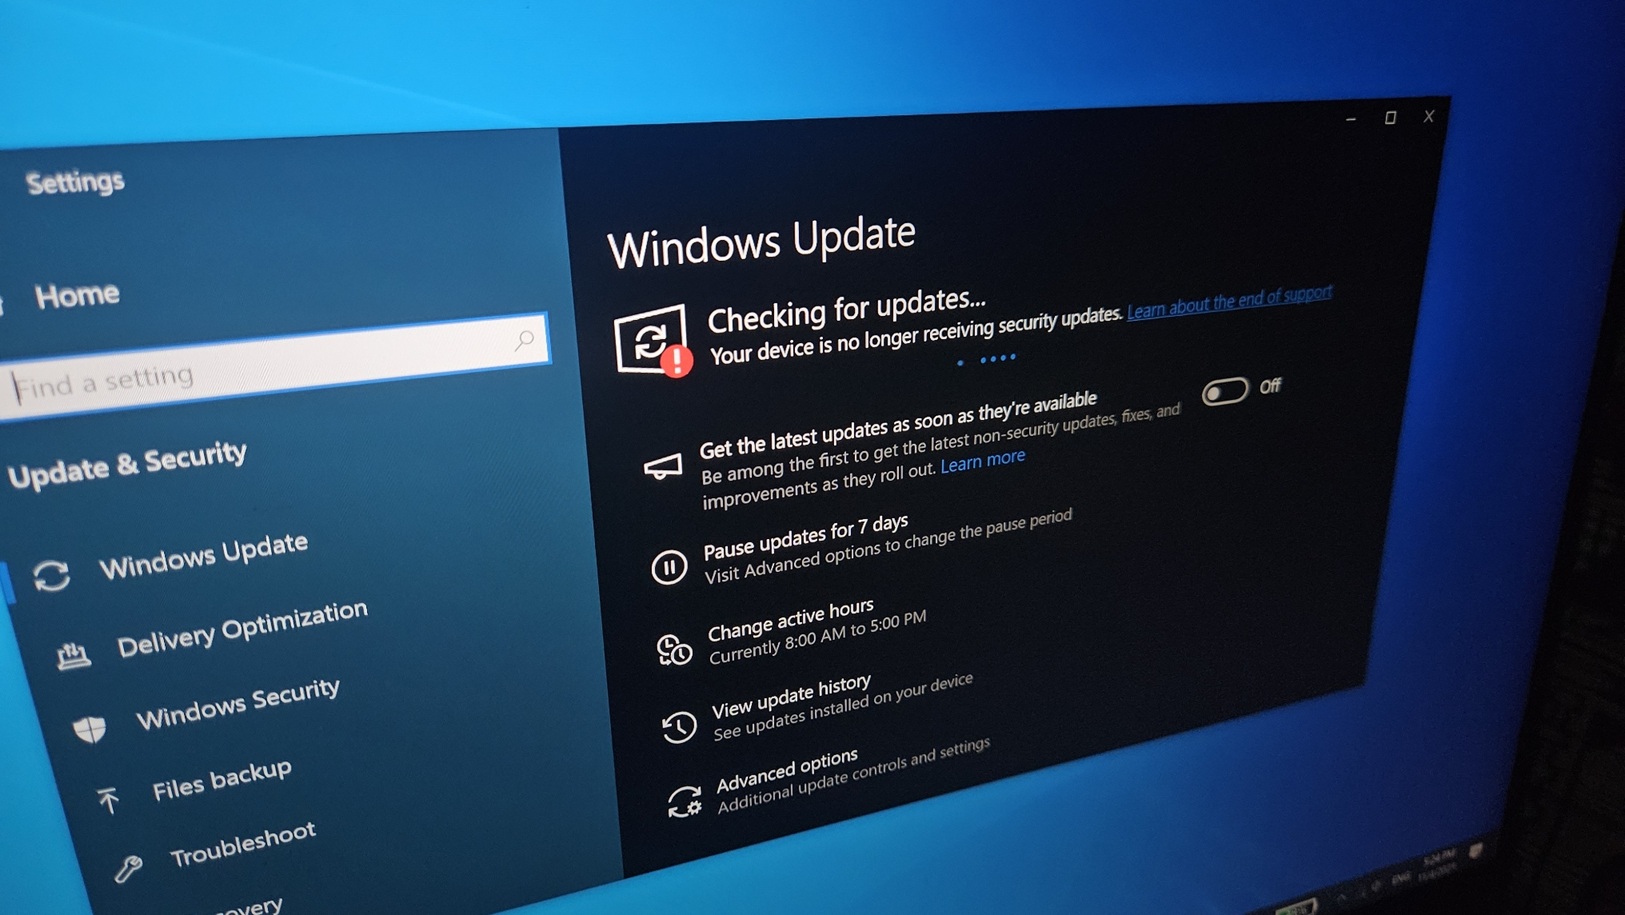
Microsoft's February 2026 security update addresses 59 vulnerabilities with 6 actively exploited zero-days, creating immediate operational and compliance risks for e-commerce sellers managing Windows-based infrastructure. Released on February 10-11, 2026, the patch addresses critical flaws in Windows Shell (CVE-2026-21510, CVSS 8.8), MSHTML Framework (CVE-2026-21513, CVSS 8.8), Microsoft Office Word (CVE-2026-21514, CVSS 7.8), Desktop Window Manager (CVE-2026-21519, CVSS 7.8), Windows Remote Access Connection Manager (CVE-2026-21525, CVSS 6.2), and Windows Remote Desktop Services (CVE-2026-21533, CVSS 7.8). The U.S. Cybersecurity and Infrastructure Security Agency (CISA) mandated federal agencies apply patches by March 3, 2026, signaling critical infrastructure vulnerability.
For e-commerce sellers, this security event creates three operational impact zones. First, seller infrastructure vulnerability: Sellers operating Windows-based order management systems, inventory databases, and accounting software face active exploitation risk. The six zero-days enable remote code execution, privilege escalation to Administrator level, and security feature bypass—allowing attackers to access customer data, payment information, and business systems. Three vulnerabilities were publicly disclosed before patching, meaning proof-of-concept exploits likely circulate online, accelerating attack adoption against unpatched systems. Second, supply chain and fulfillment disruption: Third-party logistics (3PL) providers, Amazon FBA warehouse management systems, and Shopify backend infrastructure running Windows Server components face potential compromise. A successful attack could disrupt inventory synchronization, order processing, and shipment tracking—directly impacting seller fulfillment timelines and customer satisfaction metrics. Third, compliance and liability exposure: The CISA mandate for federal agencies creates downstream pressure on government contractors and regulated industries. E-commerce sellers serving federal procurement (GSA Schedule, FedRAMP-compliant platforms) must demonstrate patch compliance within 21 days (by March 3, 2026) or risk contract suspension and liability for data breaches.
Strategic seller actions require immediate prioritization. Sellers should audit Windows systems across their technology stack—including seller central dashboards, accounting software (QuickBooks, Xero), email servers, and remote access tools—and apply patches within 7-14 days. For sellers using 3PL providers or cloud-based fulfillment, request patch status confirmation from providers immediately. Consider temporary security hardening: disable remote desktop access where possible, implement multi-factor authentication on all administrative accounts, and monitor for suspicious login attempts. Sellers with federal contracts or GSA Schedule listings must document patch deployment by March 3, 2026, to maintain compliance. The recurring Desktop Window Manager vulnerability (second consecutive month) suggests previous patches were incomplete—validate patch effectiveness through security scanning before resuming normal operations. This security event underscores the operational dependency e-commerce sellers have on Microsoft infrastructure and the cascading impact of enterprise vulnerabilities on cross-border commerce operations.
Questions 8
What are the financial and operational costs of not patching these vulnerabilities?
The financial impact of a breach from these vulnerabilities could be severe: (1) Direct costs: Data breach notification (averaging $4.45M per breach in 2024), regulatory fines (GDPR fines up to 4% of revenue), and customer compensation; (2) Operational costs: System downtime during incident response (averaging 21 days), lost sales during outages, and fulfillment delays; (3) Reputational costs: Customer churn, loss of buy box eligibility on Amazon, and suspension from federal procurement. The news confirms these vulnerabilities are actively exploited in the wild, meaning breach probability is elevated. For sellers with $1M+ annual revenue, a single breach could cost 10-20% of annual revenue. Patching costs approximately 4-8 hours of IT labor per system, making it a highly cost-effective risk mitigation compared to breach costs.
Why is the recurring Desktop Window Manager vulnerability concerning for sellers?
The news specifically notes that CVE-2026-21519 (Desktop Window Manager elevation-of-privilege flaw) marks the second consecutive month DWM vulnerabilities appeared in active exploitation. This pattern suggests previous patches were incomplete or attackers discovered bypass techniques. For sellers, this indicates elevated risk that initial patch deployment may not fully resolve the vulnerability. The news recommends thorough validation of fixes before full deployment. Sellers should apply patches, then conduct security scanning 48-72 hours later to verify the vulnerability is actually remediated. If scanning still detects DWM vulnerabilities, escalate to Microsoft support or consider temporary workarounds like disabling visual themes or using alternative remote access methods.