

)


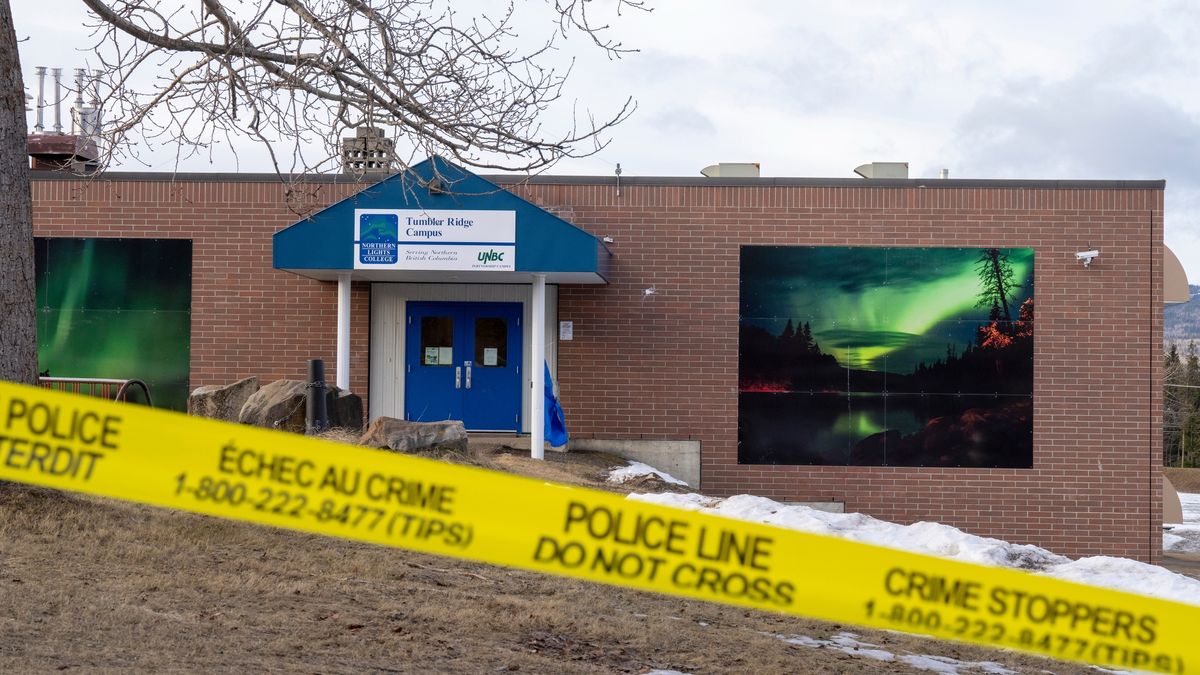
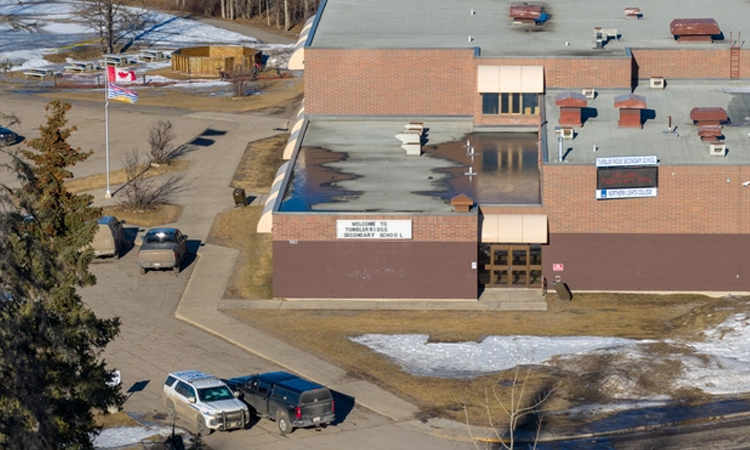
OpenAI's comprehensive safety protocol overhaul following the February 2025 Tumbler Ridge, British Columbia mass shooting represents a watershed moment for AI regulation that directly impacts cross-border e-commerce sellers. The incident—where suspect Jesse Van Rootselaar maintained two ChatGPT accounts despite one being flagged in June 2024—exposed critical gaps in AI platform detection systems. OpenAI's response includes revised threat assessment criteria (now requiring law enforcement notification for any dangerous conversation, not just imminent threats with specific targets), technical measures preventing banned users from creating new accounts, and direct law enforcement contact points. This regulatory shift signals that governments worldwide will increasingly mandate AI platform accountability, with implications for sellers using AI tools in customer service, content moderation, and business analytics.
For e-commerce sellers, the operational impact is substantial. Sellers operating in Canada or serving Canadian customers using AI-powered chatbots for customer service must now anticipate stricter account monitoring and potential law enforcement data sharing. This affects data privacy practices, account security requirements, and compliance obligations. The shift toward "flexible" law enforcement referral criteria means AI platforms will report suspicious account activities more aggressively—potentially capturing legitimate business communications flagged as concerning. Sellers should expect increased scrutiny of customer interaction patterns, particularly for high-volume sellers managing thousands of daily conversations through AI tools. The Canadian government's threat of regulatory action if tech companies cannot demonstrate adequate safeguards suggests mandatory compliance frameworks may follow within 12-18 months, similar to GDPR implementation timelines.
Strategic implications extend beyond Canada. BC Premier David Eby's call for "national reporting standards comparable to duty-of-care obligations" mirrors healthcare and social work regulations, suggesting future AI legislation could impose liability on sellers using AI tools without proper safeguards. The government's "disappointing" assessment of OpenAI's initial response indicates regulatory expectations exceed current industry standards. Sellers relying on AI for customer service automation, content moderation, or business analytics should prepare for similar protocol changes across US, EU, and Asia-Pacific jurisdictions. The incident demonstrates that AI platforms will prioritize law enforcement cooperation over user privacy when safety concerns emerge, fundamentally changing the risk calculus for sellers using these tools for sensitive customer data processing.
The news reports that BC Premier Eby emphasized the need for duty-of-care obligations comparable to healthcare and social work standards. This signals potential future seller liability if customers misuse AI tools accessed through seller platforms or services. Currently, sellers have limited liability for customer misuse of third-party tools; however, the regulatory trend suggests this will change. If a seller knowingly provides AI tools without adequate safeguards and a customer uses them for harmful purposes, future regulations may impose liability on the seller. Sellers should implement reasonable safeguards: terms of service prohibiting illegal use, monitoring for suspicious patterns, and cooperation with law enforcement requests. Document all safety measures taken. This is particularly important for sellers in high-risk categories (weapons, chemicals, sensitive information) where AI tool misuse could facilitate harm. Consult legal counsel in your jurisdiction about emerging liability standards.
Sellers should immediately conduct three audits: (1) Inventory all AI tools used in customer service, content moderation, and business analytics; (2) Review data flows to identify what customer information is processed by AI systems; (3) Document current safety measures and identify gaps. Implement immediate controls: disable AI-powered customer service for sensitive topics (payment methods, personal health information), establish clear content policies prohibiting violent or illegal discussions, and train customer service teams on appropriate AI tool usage. Update privacy policies to disclose AI processing to customers. For Canadian sellers, this is urgent; for others, complete these steps by March 31, 2025. Establish a compliance monitoring process: monthly reviews of AI tool updates, quarterly audits of customer interaction patterns, and documentation of any law enforcement inquiries. Budget 40-80 hours for initial compliance work; ongoing monitoring requires 5-10 hours monthly depending on business size.
No, but sellers should use AI tools strategically with appropriate safeguards. The news reports OpenAI is implementing enhanced detection systems and safety measures—the platform is becoming more trustworthy, not less. The incident demonstrates that AI tools can be valuable when used responsibly with proper oversight. Sellers should continue using AI for appropriate applications: product recommendations, FAQ responses, order status inquiries, and routine customer service. Avoid using AI for sensitive topics: payment processing, personal health information, legal advice, or discussions involving potential harm. Implement human review for high-risk interactions. The regulatory trend suggests AI tools with strong safety features will become industry standard; sellers avoiding AI entirely may face competitive disadvantages. Instead, adopt a risk-based approach: use AI for low-risk applications, implement safeguards for medium-risk uses, and avoid high-risk applications. This balanced strategy positions sellers to comply with emerging regulations while maintaining operational efficiency.
Initial compliance costs include: audit and documentation (40-80 hours at $50-150/hour = $2,000-12,000), policy updates and legal review ($1,000-5,000), staff training ($500-2,000), and potential tool replacement or modification ($1,000-10,000 depending on current AI infrastructure). Ongoing costs include monthly monitoring (5-10 hours = $250-1,500/month), quarterly audits ($500-2,000/quarter), and potential law enforcement cooperation resources ($100-500/incident). For small sellers (under $100K annual revenue), total first-year costs are typically $5,000-20,000; medium sellers ($100K-$1M) face $15,000-40,000; large sellers ($1M+) may invest $50,000-150,000+ depending on AI tool complexity. The news indicates government regulatory action is imminent, making early compliance investment cost-effective compared to reactive compliance after regulations are mandated. Consider compliance costs when evaluating AI tool ROI; tools requiring extensive safety infrastructure may not be cost-justified for small sellers.
Based on regulatory precedent (GDPR compliance averaged $1-2M for mid-size companies), sellers should budget 5-15% operational cost increases for AI compliance. Specific costs include: compliance documentation and audit procedures ($2,000-5,000 initial setup), staff training on acceptable AI usage ($500-1,500 per employee), content review processes for AI-generated materials ($1,000-3,000 monthly for mid-size sellers), alternative AI tool subscriptions ($50-200 monthly), and legal consultation for liability assessment ($3,000-10,000). Larger sellers (100+ employees) should budget $50,000-150,000 annually for comprehensive compliance infrastructure. Smaller sellers (1-10 employees) can implement basic compliance for $5,000-15,000 annually. These costs will increase if Canadian regulatory requirements mandate formal certifications, audits, or licensing—potentially adding 20-30% to compliance budgets. Start budgeting immediately as regulatory requirements will likely take effect within 12 months.
OpenAI's revised threat assessment criteria now require law enforcement notification for any dangerous conversation, not just imminent threats with specific targets. This means sellers' customer service interactions using ChatGPT may be flagged and reported to authorities if the AI system detects concerning language patterns. Sellers should audit their customer service workflows immediately, implement clear policies prohibiting violent or illegal content discussions, and document legitimate business communications. The company is establishing direct law enforcement contact points, meaning data sharing can occur rapidly without seller notification. Sellers in Canada face immediate compliance requirements; US and EU sellers should expect similar regulations within 12-18 months as governments adopt comparable standards.
The Canadian government's threat of regulatory action if tech companies cannot demonstrate adequate safeguards suggests mandatory compliance frameworks will follow within 12-18 months. BC Premier David Eby's call for national reporting standards comparable to healthcare duty-of-care obligations indicates governments are moving toward legislated requirements rather than voluntary compliance. The EU's AI Act already establishes risk-based frameworks; this incident will likely accelerate implementation of high-risk AI use case restrictions. US regulation typically follows 18-24 months behind EU standards. Sellers should prepare compliance strategies now: audit AI tool usage, document safety measures, establish data governance policies, and consider alternative tools for sensitive applications. The incident demonstrates that reactive compliance (after problems emerge) is insufficient; proactive safety documentation will become a competitive advantage.
OpenAI's commitment to establish direct law enforcement contact points for real-time information sharing means customer interaction data may be disclosed to authorities without seller consent or advance notice. This creates significant privacy risks for sellers handling sensitive customer information through AI-powered systems. The news reports that the company will now refer users to mental health resources when distress is detected—a positive safety measure but one that requires analyzing conversation content. Sellers should assume all customer service conversations using ChatGPT are subject to law enforcement review. Implement data minimization practices: avoid storing unnecessary customer information in AI systems, use separate tools for sensitive transactions, and consider privacy-first alternatives for customer service in regulated industries (healthcare, finance). Document your data handling practices to demonstrate compliance if regulators inquire.
The news reports that BC Premier Eby emphasized the need for duty-of-care obligations comparable to healthcare and social work standards. This signals potential future seller liability if customers misuse AI tools accessed through seller platforms or services. Currently, sellers have limited liability for customer misuse of third-party tools; however, the regulatory trend suggests this will change. If a seller knowingly provides AI tools without adequate safeguards and a customer uses them for harmful purposes, future regulations may impose liability on the seller. Sellers should implement reasonable safeguards: terms of service prohibiting illegal use, monitoring for suspicious patterns, and cooperation with law enforcement requests. Document all safety measures taken. This is particularly important for sellers in high-risk categories (weapons, chemicals, sensitive information) where AI tool misuse could facilitate harm. Consult legal counsel in your jurisdiction about emerging liability standards.
Sellers should immediately conduct three audits: (1) Inventory all AI tools used in customer service, content moderation, and business analytics; (2) Review data flows to identify what customer information is processed by AI systems; (3) Document current safety measures and identify gaps. Implement immediate controls: disable AI-powered customer service for sensitive topics (payment methods, personal health information), establish clear content policies prohibiting violent or illegal discussions, and train customer service teams on appropriate AI tool usage. Update privacy policies to disclose AI processing to customers. For Canadian sellers, this is urgent; for others, complete these steps by March 31, 2025. Establish a compliance monitoring process: monthly reviews of AI tool updates, quarterly audits of customer interaction patterns, and documentation of any law enforcement inquiries. Budget 40-80 hours for initial compliance work; ongoing monitoring requires 5-10 hours monthly depending on business size.
No, but sellers should use AI tools strategically with appropriate safeguards. The news reports OpenAI is implementing enhanced detection systems and safety measures—the platform is becoming more trustworthy, not less. The incident demonstrates that AI tools can be valuable when used responsibly with proper oversight. Sellers should continue using AI for appropriate applications: product recommendations, FAQ responses, order status inquiries, and routine customer service. Avoid using AI for sensitive topics: payment processing, personal health information, legal advice, or discussions involving potential harm. Implement human review for high-risk interactions. The regulatory trend suggests AI tools with strong safety features will become industry standard; sellers avoiding AI entirely may face competitive disadvantages. Instead, adopt a risk-based approach: use AI for low-risk applications, implement safeguards for medium-risk uses, and avoid high-risk applications. This balanced strategy positions sellers to comply with emerging regulations while maintaining operational efficiency.
Initial compliance costs include: audit and documentation (40-80 hours at $50-150/hour = $2,000-12,000), policy updates and legal review ($1,000-5,000), staff training ($500-2,000), and potential tool replacement or modification ($1,000-10,000 depending on current AI infrastructure). Ongoing costs include monthly monitoring (5-10 hours = $250-1,500/month), quarterly audits ($500-2,000/quarter), and potential law enforcement cooperation resources ($100-500/incident). For small sellers (under $100K annual revenue), total first-year costs are typically $5,000-20,000; medium sellers ($100K-$1M) face $15,000-40,000; large sellers ($1M+) may invest $50,000-150,000+ depending on AI tool complexity. The news indicates government regulatory action is imminent, making early compliance investment cost-effective compared to reactive compliance after regulations are mandated. Consider compliance costs when evaluating AI tool ROI; tools requiring extensive safety infrastructure may not be cost-justified for small sellers.
Based on regulatory precedent (GDPR compliance averaged $1-2M for mid-size companies), sellers should budget 5-15% operational cost increases for AI compliance. Specific costs include: compliance documentation and audit procedures ($2,000-5,000 initial setup), staff training on acceptable AI usage ($500-1,500 per employee), content review processes for AI-generated materials ($1,000-3,000 monthly for mid-size sellers), alternative AI tool subscriptions ($50-200 monthly), and legal consultation for liability assessment ($3,000-10,000). Larger sellers (100+ employees) should budget $50,000-150,000 annually for comprehensive compliance infrastructure. Smaller sellers (1-10 employees) can implement basic compliance for $5,000-15,000 annually. These costs will increase if Canadian regulatory requirements mandate formal certifications, audits, or licensing—potentially adding 20-30% to compliance budgets. Start budgeting immediately as regulatory requirements will likely take effect within 12 months.
OpenAI's revised threat assessment criteria now require law enforcement notification for any dangerous conversation, not just imminent threats with specific targets. This means sellers' customer service interactions using ChatGPT may be flagged and reported to authorities if the AI system detects concerning language patterns. Sellers should audit their customer service workflows immediately, implement clear policies prohibiting violent or illegal content discussions, and document legitimate business communications. The company is establishing direct law enforcement contact points, meaning data sharing can occur rapidly without seller notification. Sellers in Canada face immediate compliance requirements; US and EU sellers should expect similar regulations within 12-18 months as governments adopt comparable standards.
The Canadian government's threat of regulatory action if tech companies cannot demonstrate adequate safeguards suggests mandatory compliance frameworks will follow within 12-18 months. BC Premier David Eby's call for national reporting standards comparable to healthcare duty-of-care obligations indicates governments are moving toward legislated requirements rather than voluntary compliance. The EU's AI Act already establishes risk-based frameworks; this incident will likely accelerate implementation of high-risk AI use case restrictions. US regulation typically follows 18-24 months behind EU standards. Sellers should prepare compliance strategies now: audit AI tool usage, document safety measures, establish data governance policies, and consider alternative tools for sensitive applications. The incident demonstrates that reactive compliance (after problems emerge) is insufficient; proactive safety documentation will become a competitive advantage.
OpenAI's commitment to establish direct law enforcement contact points for real-time information sharing means customer interaction data may be disclosed to authorities without seller consent or advance notice. This creates significant privacy risks for sellers handling sensitive customer information through AI-powered systems. The news reports that the company will now refer users to mental health resources when distress is detected—a positive safety measure but one that requires analyzing conversation content. Sellers should assume all customer service conversations using ChatGPT are subject to law enforcement review. Implement data minimization practices: avoid storing unnecessary customer information in AI systems, use separate tools for sensitive transactions, and consider privacy-first alternatives for customer service in regulated industries (healthcare, finance). Document your data handling practices to demonstrate compliance if regulators inquire.
The news reports that BC Premier Eby emphasized the need for duty-of-care obligations comparable to healthcare and social work standards. This signals potential future seller liability if customers misuse AI tools accessed through seller platforms or services. Currently, sellers have limited liability for customer misuse of third-party tools; however, the regulatory trend suggests this will change. If a seller knowingly provides AI tools without adequate safeguards and a customer uses them for harmful purposes, future regulations may impose liability on the seller. Sellers should implement reasonable safeguards: terms of service prohibiting illegal use, monitoring for suspicious patterns, and cooperation with law enforcement requests. Document all safety measures taken. This is particularly important for sellers in high-risk categories (weapons, chemicals, sensitive information) where AI tool misuse could facilitate harm. Consult legal counsel in your jurisdiction about emerging liability standards.
Sellers should immediately conduct three audits: (1) Inventory all AI tools used in customer service, content moderation, and business analytics; (2) Review data flows to identify what customer information is processed by AI systems; (3) Document current safety measures and identify gaps. Implement immediate controls: disable AI-powered customer service for sensitive topics (payment methods, personal health information), establish clear content policies prohibiting violent or illegal discussions, and train customer service teams on appropriate AI tool usage. Update privacy policies to disclose AI processing to customers. For Canadian sellers, this is urgent; for others, complete these steps by March 31, 2025. Establish a compliance monitoring process: monthly reviews of AI tool updates, quarterly audits of customer interaction patterns, and documentation of any law enforcement inquiries. Budget 40-80 hours for initial compliance work; ongoing monitoring requires 5-10 hours monthly depending on business size.