



Iran Cyber Threats Escalate | E-Commerce Sellers Face Payment & Infrastructure Risks
- State-sponsored hackers target US datacenters and payment systems since February 28; sellers relying on US cloud infrastructure face business continuity threats











Overview
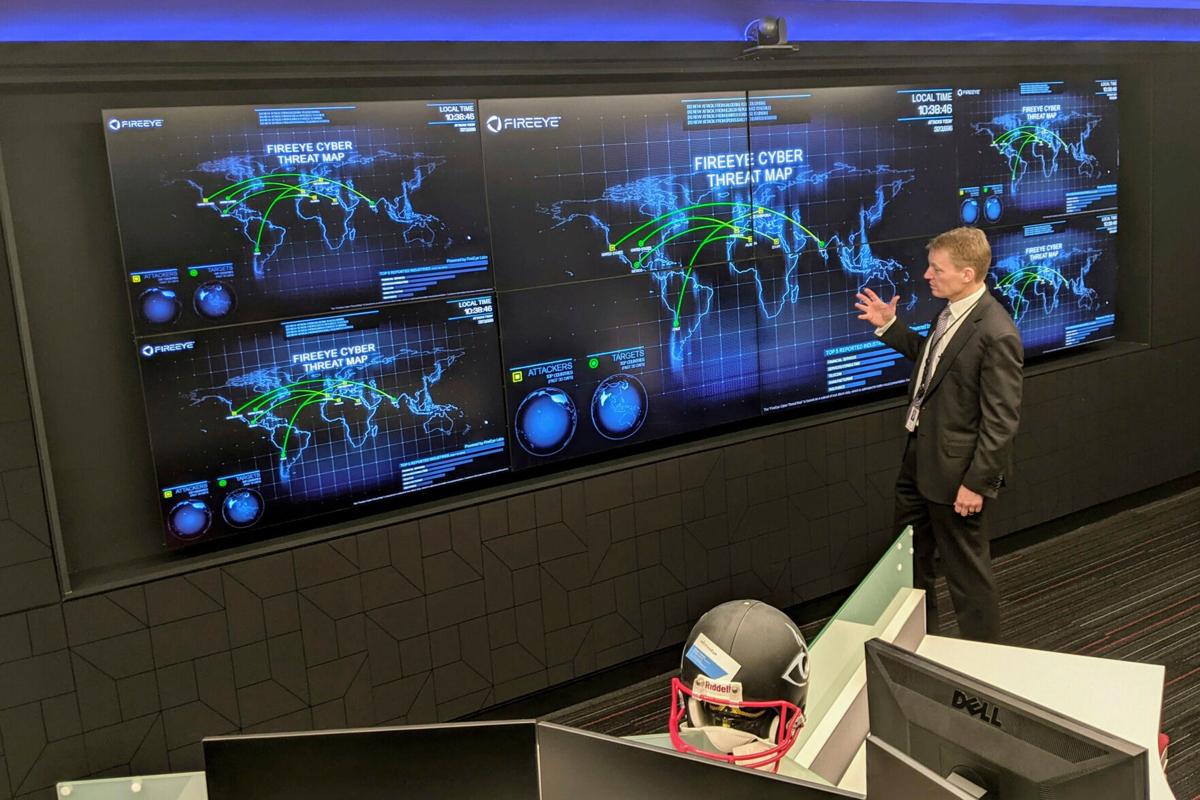
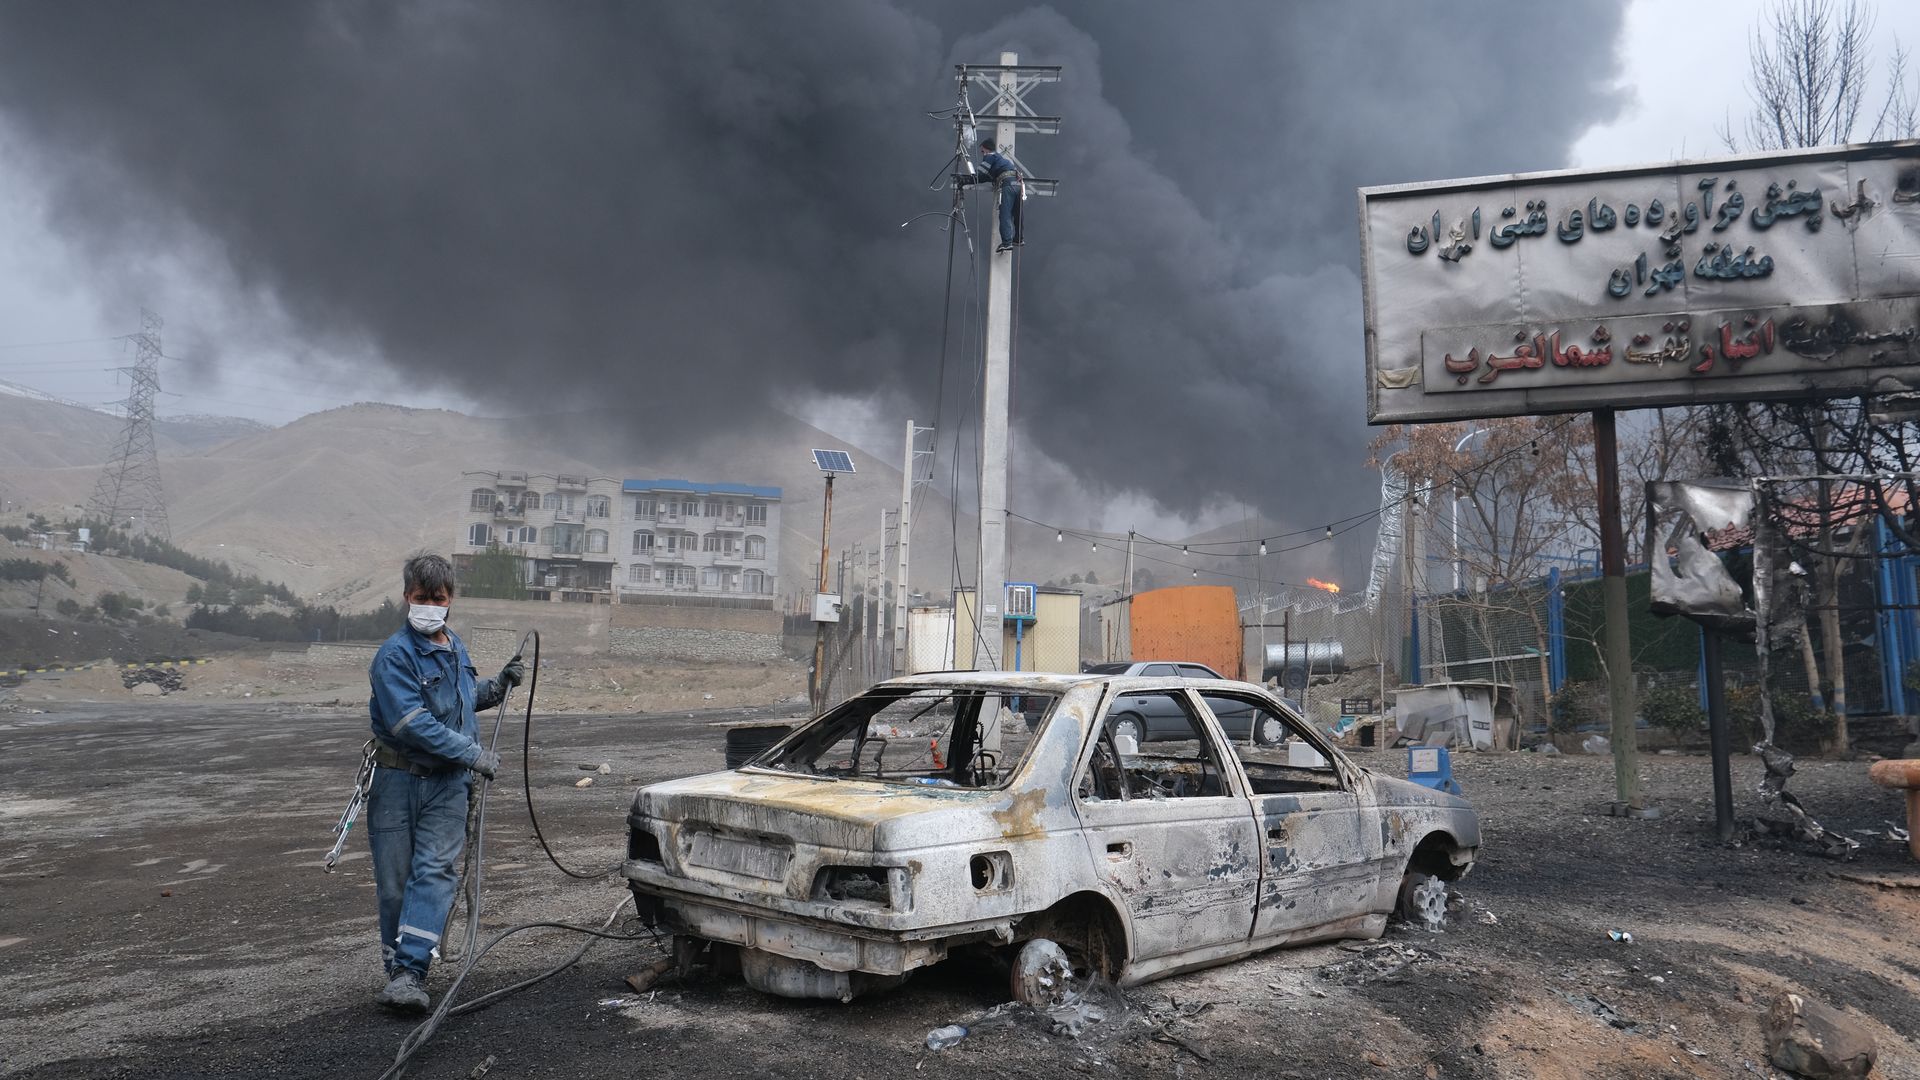
Iranian state-sponsored cyber operations have intensified dramatically since February 28, 2025, creating direct operational risks for cross-border e-commerce sellers. According to AP News reporting and cybersecurity experts including Kevin Mandia (Mandiant founder), pro-Iranian hacking groups including the Handala collective have launched coordinated attacks against US critical infrastructure, defense contractors, and datacenters. The threat landscape has shifted from isolated incidents to integrated hybrid warfare tactics combining military escalation with synchronized cyber operations. CrowdStrike researchers detected surge activity from Russian hackers supporting Tehran, with group Z-Pentest claiming responsibility for disrupting US networks including closed-circuit video systems and infrastructure control networks.
For e-commerce sellers, the operational impact is substantial and multifaceted. The news explicitly identifies three critical vulnerabilities: (1) Payment processing disruptions - Iranian hackers have targeted financial institutions and payment infrastructure, directly threatening transaction processing for sellers using US-based payment gateways like Stripe, PayPal, and Amazon Pay; (2) Cloud infrastructure concentration risk - Pro-Iranian hackers openly discuss plans on Telegram to "take out datacenters" hosting US military communication systems, creating collateral risk for sellers relying on AWS, Google Cloud, or Azure infrastructure in US regions; (3) Supply chain logistics disruption - Attacks on ports, water plants, and transportation infrastructure could delay shipments and increase logistics costs for sellers dependent on US fulfillment networks. Stryker's cyberattack (Michigan-based medical device company) demonstrates attackers' capability to penetrate major US corporations, signaling broader vulnerability across commercial infrastructure.
Immediate seller implications span three operational domains. First, data security exposure - Hack-and-leak operations threaten sensitive seller data including customer information, payment records, and business communications. Sellers storing customer data in US datacenters face elevated risk of breach and regulatory penalties under GDPR and CCPA. Second, business continuity threats - Denial-of-service attacks could temporarily disable seller storefronts, payment processing, and inventory management systems. The Department of Homeland Security's 2024 public warnings about Iranian cyber threats indicate sustained operational capability. Third, infrastructure diversification costs - Sellers currently concentrated in single US cloud regions face pressure to migrate to multi-region deployments or alternative providers, incurring 15-25% infrastructure cost increases during transition periods.
Strategic risk mitigation requires immediate action. Sellers should implement the cybersecurity protocols emphasized by industry experts: multi-factor authentication across all seller accounts, regular security audits of payment processing integrations, and incident response planning with documented failover procedures. Consider diversifying fulfillment infrastructure across multiple geographic regions—shifting 20-30% of inventory to non-US 3PL providers reduces concentration risk. Monitor Amazon Seller Central security notifications and enable all available account protection features. For sellers with significant US operations, evaluate alternative payment processors with redundant infrastructure or consider geographic diversification of customer bases toward EU and Asia-Pacific markets where infrastructure risk profiles differ.
Questions 8
How do Iranian cyber attacks directly impact e-commerce sellers' payment processing?
Iranian hackers have targeted financial institutions and payment infrastructure, creating direct risk for sellers using US-based payment gateways like Stripe, PayPal, and Amazon Pay. The news reports that pro-Iranian groups openly discuss plans to disrupt US datacenters hosting critical infrastructure. Sellers relying on single payment processors face transaction processing interruptions during attacks. Implement redundant payment processing with multiple gateway providers and enable multi-factor authentication on all payment accounts. Monitor your payment processor's security status through their status pages and maintain backup payment methods for customer transactions.
What is the risk to sellers using AWS, Google Cloud, or Azure for inventory management?
Pro-Iranian hackers explicitly target US datacenters, with Telegram discussions stating 'datacenters need to be taken out' as they host US military communication systems. Sellers concentrating inventory management, customer data, and order processing in single US cloud regions face elevated disruption risk. The Stryker cyberattack demonstrates attackers can penetrate major US corporations. Diversify infrastructure across multiple geographic regions—consider migrating 20-30% of critical systems to EU or Asia-Pacific cloud regions. This typically costs 15-25% more during transition but reduces concentration risk significantly.