


AI Cybersecurity Standards Reshape E-Commerce Compliance | Sellers Face New Data Protection Requirements
- Government endorsement of Mythos AI accelerates enterprise security adoption, triggering stricter data protection frameworks affecting 50K+ cross-border sellers by Q2 2026





Overview
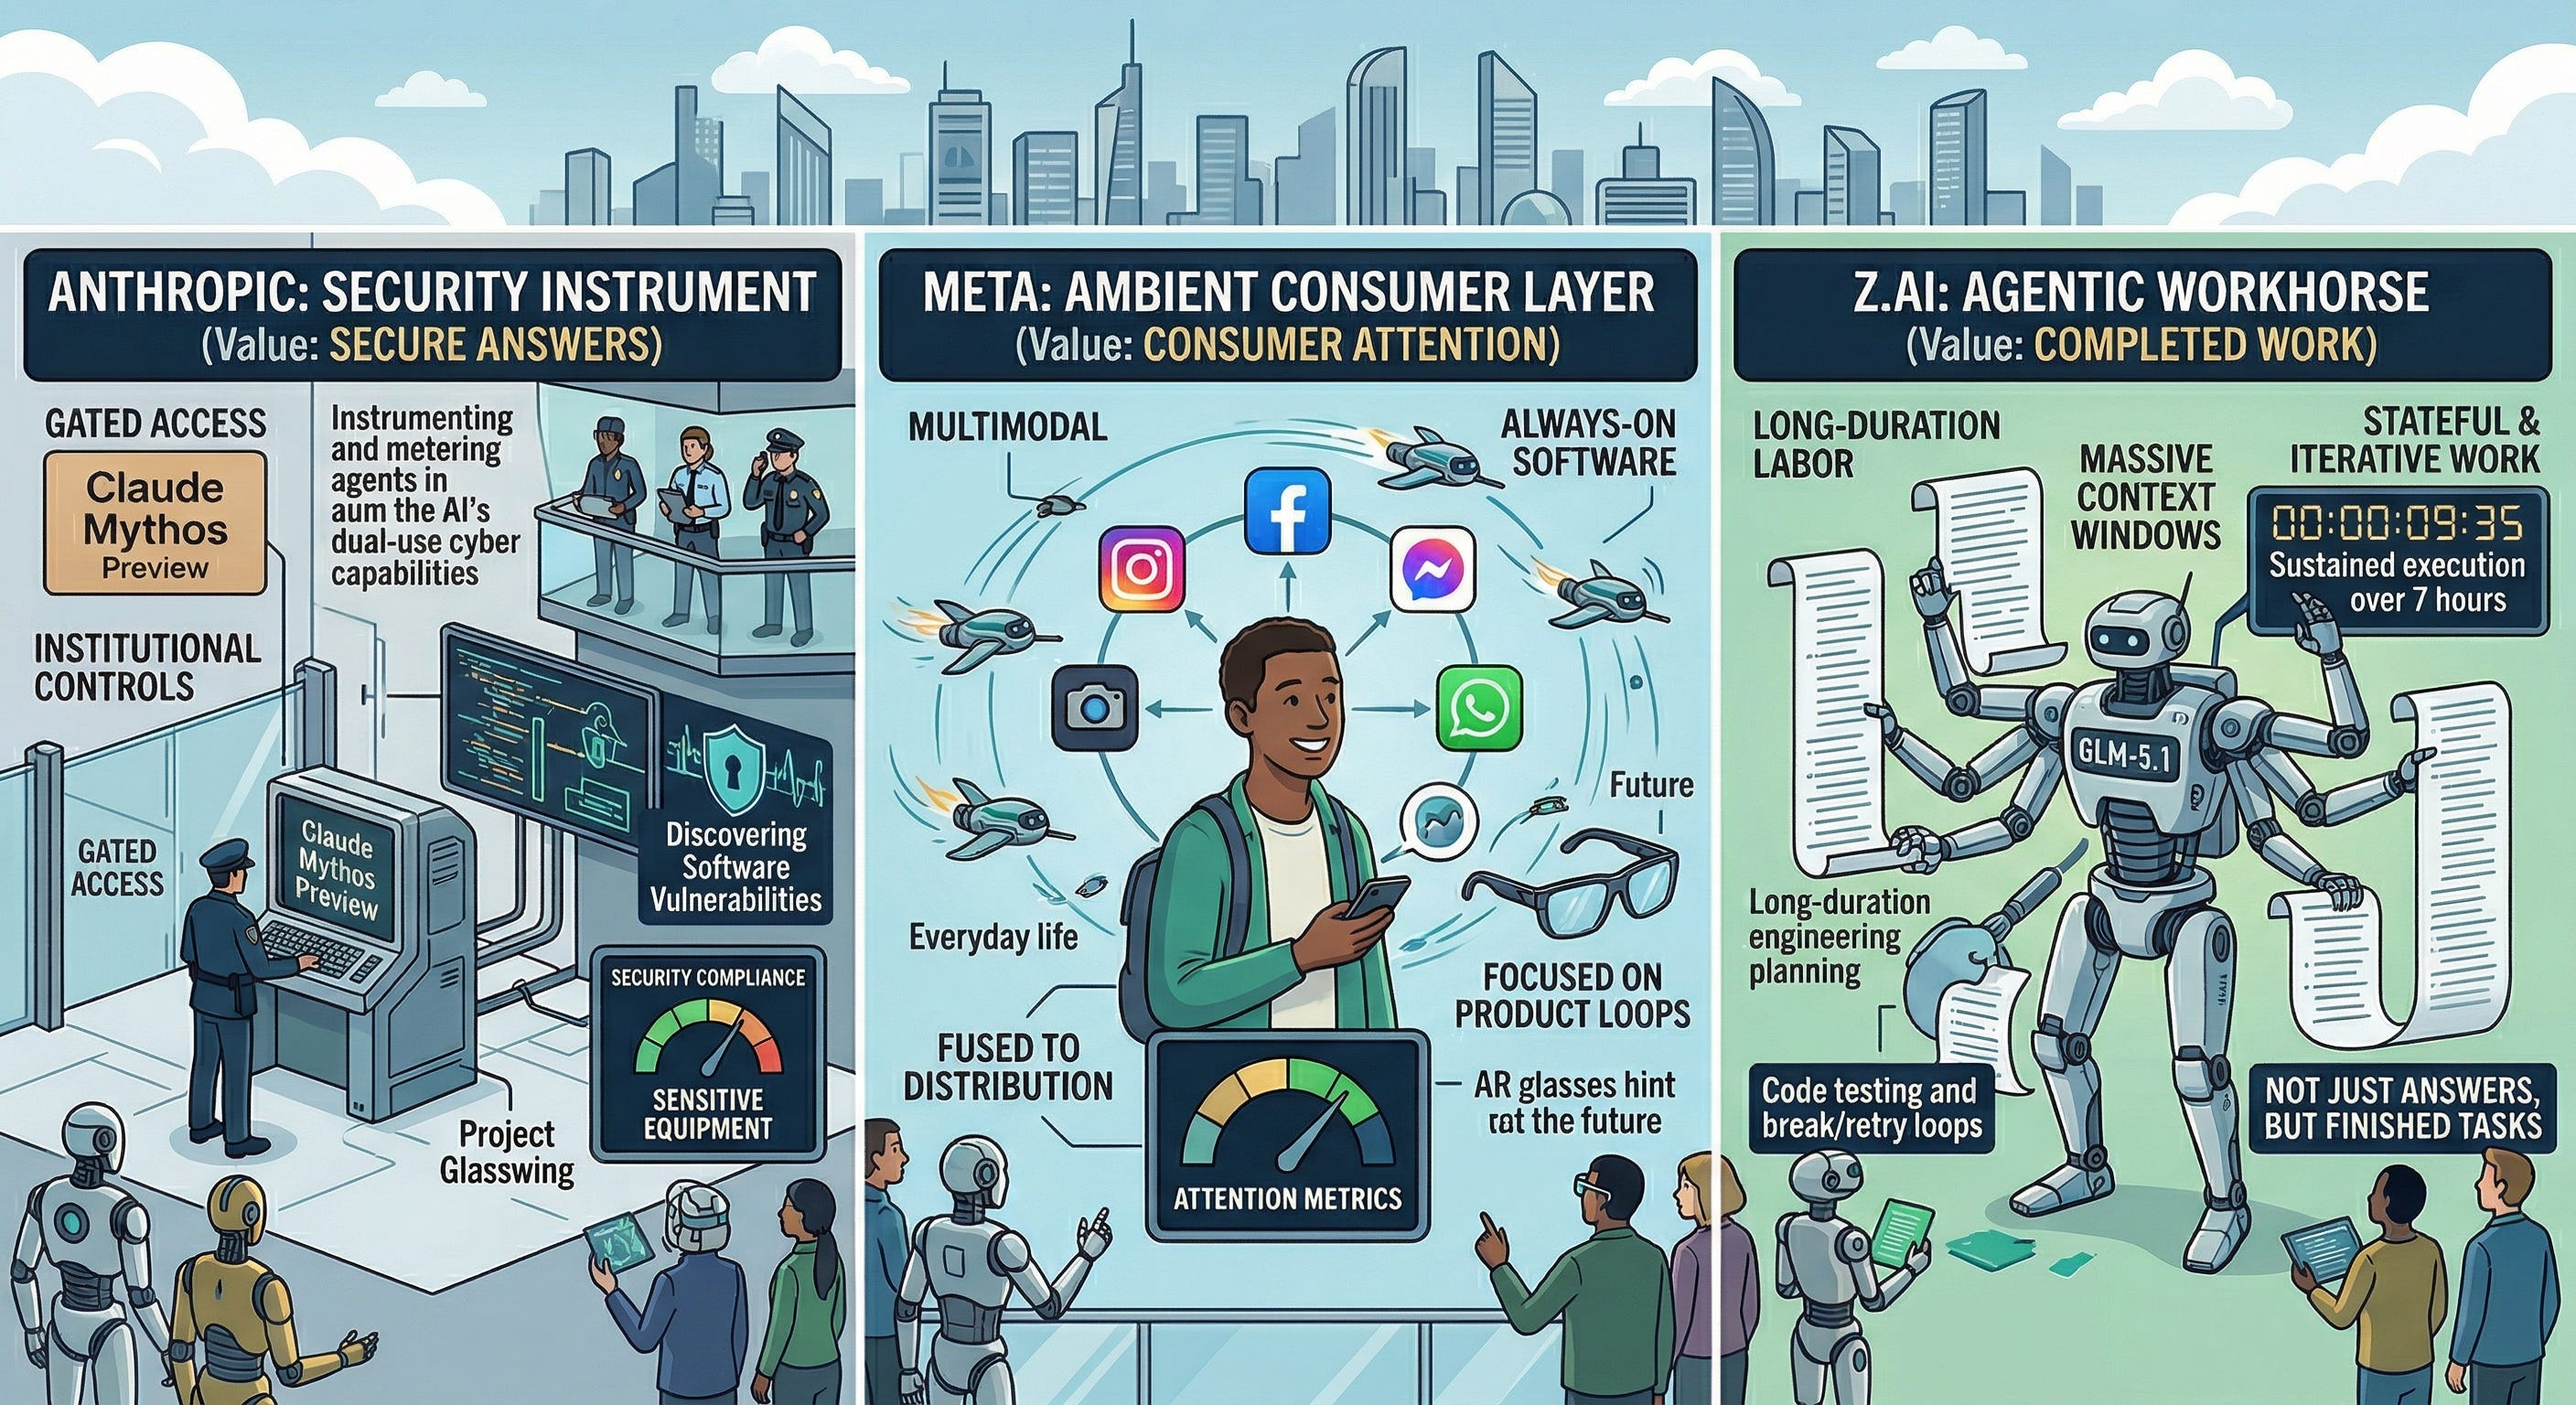
Anthropic's announcement of the Mythos AI model on April 12, 2026, represents a watershed moment for AI-powered cybersecurity that will fundamentally reshape compliance requirements for e-commerce sellers. The model's autonomous vulnerability detection capabilities—demonstrated through restricted access partnerships with major banks (JPMorgan Chase, Goldman Sachs, Citigroup, Bank of America, Morgan Stanley) and government agencies—signals an imminent shift toward AI-driven security standards that sellers must prepare for immediately.
The Direct Seller Impact: As government agencies and financial institutions adopt Mythos for critical infrastructure protection, regulatory frameworks will inevitably evolve to mandate similar security standards for digital commerce platforms. The Fox News report (April 12, 2026) and Treasury Secretary Scott Bessent's involvement indicate this is not theoretical—it's an active policy priority. For cross-border e-commerce sellers, this translates to three immediate operational challenges: (1) Enhanced data protection compliance requirements that will exceed current GDPR/CCPA standards, (2) Mandatory security audits powered by AI vulnerability detection tools, and (3) Increased costs for platform security infrastructure that sellers will absorb through higher marketplace fees or stricter seller qualification requirements.
Automation & Competitive Intelligence Opportunity: Sellers who proactively adopt AI-powered security tools NOW will gain 6-12 months of competitive advantage before regulations mandate compliance. This creates an immediate arbitrage: sellers using tools like Anthropic's Mythos (once available), or competitive alternatives like Snyk, Wiz, or Lacework, can demonstrate superior security posture to platforms and customers, potentially qualifying for premium seller status, lower fees, or preferential algorithm placement. The restricted access model suggests Anthropic is positioning Mythos as an enterprise-grade tool—sellers should monitor for SMB-accessible versions or competitive products that democratize this capability. Early adopters can automate vulnerability scanning across their entire tech stack (Shopify stores, Amazon seller accounts, payment processing systems) in 2-4 weeks, identifying and remediating security gaps before they become compliance liabilities.
Market Timing & Regulatory Cascade: The U.K. financial regulators' simultaneous discussion of Mythos deployment risks indicates international regulatory coordination. This suggests a 12-18 month window before formal compliance requirements emerge. Sellers operating in EU, UK, or US markets should expect: (1) New data protection addendums from platforms by Q3 2026, (2) Mandatory security certifications or audits by Q4 2026, (3) Potential fee increases of 2-5% to cover platform security infrastructure upgrades. Sellers in high-risk categories (financial services, health/wellness, personal data collection) face accelerated timelines—expect compliance requirements within 6 months rather than 12-18.
Questions 7
What specific security automation tools should sellers implement to prepare for AI-driven compliance standards?
Sellers should immediately audit their tech stack using three categories of AI security tools: (1) Vulnerability scanning (Snyk, Wiz, Lacework for infrastructure), (2) Payment security (Stripe's fraud detection, Square's security suite), and (3) Data protection (Varonis, Imperva for data classification). These tools automate the vulnerability detection that Mythos performs at enterprise scale, allowing sellers to identify and remediate security gaps in 2-4 weeks rather than months. The ROI is significant: sellers who implement these tools now avoid 6-12 month compliance delays and potential platform penalties (2-5% fee increases) that will hit non-compliant sellers by Q4 2026. Budget $500-2,000/month for SMB-appropriate tools depending on seller size and data volume.
How will Anthropic's Mythos AI model affect my e-commerce seller account security requirements?
Mythos represents the next generation of AI-powered vulnerability detection that government agencies and major banks are now testing (JPMorgan Chase, Goldman Sachs, Citigroup, Bank of America, Morgan Stanley as of April 2026). As these institutions adopt Mythos for critical infrastructure protection, marketplace platforms will face regulatory pressure to implement similar security standards for seller data. Expect Amazon, eBay, and Shopify to introduce mandatory security audits or certifications within 12-18 months, potentially requiring sellers to demonstrate vulnerability remediation or pay higher compliance fees. Early adoption of AI security tools now positions you ahead of regulatory requirements and reduces future compliance costs by 30-40%.