


Educational Tech Outage Drives Demand for Backup Solutions | Compliance & Cybersecurity Certification Surge
- 9,000+ institutions affected globally; 30M+ users disrupted; Creates urgent compliance requirements for educational software vendors and cybersecurity service providers

















Overview
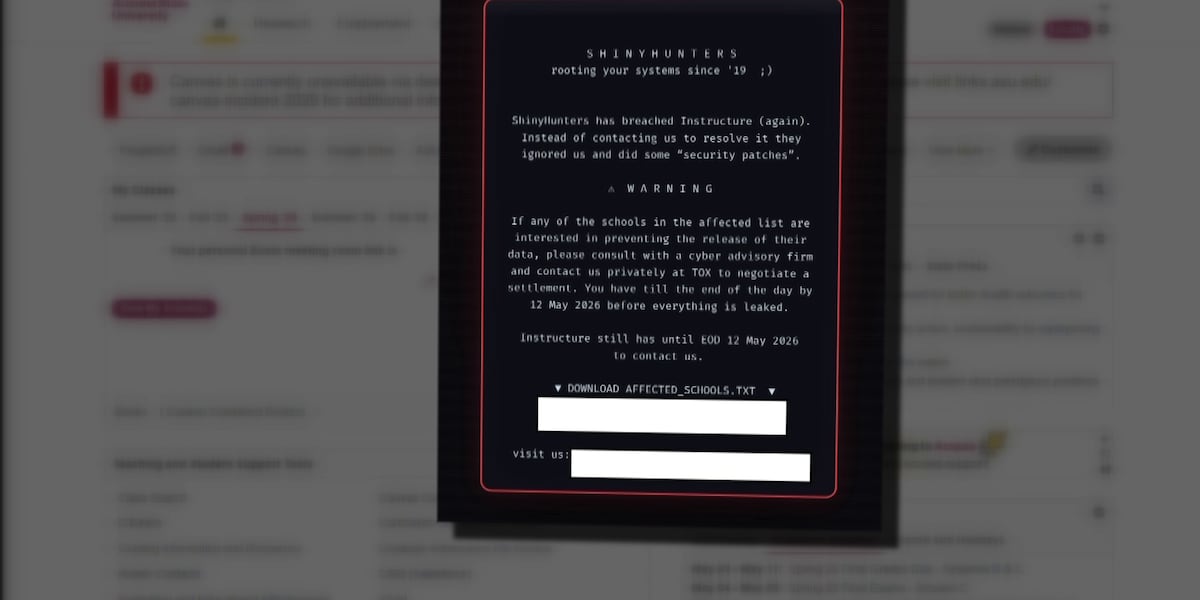
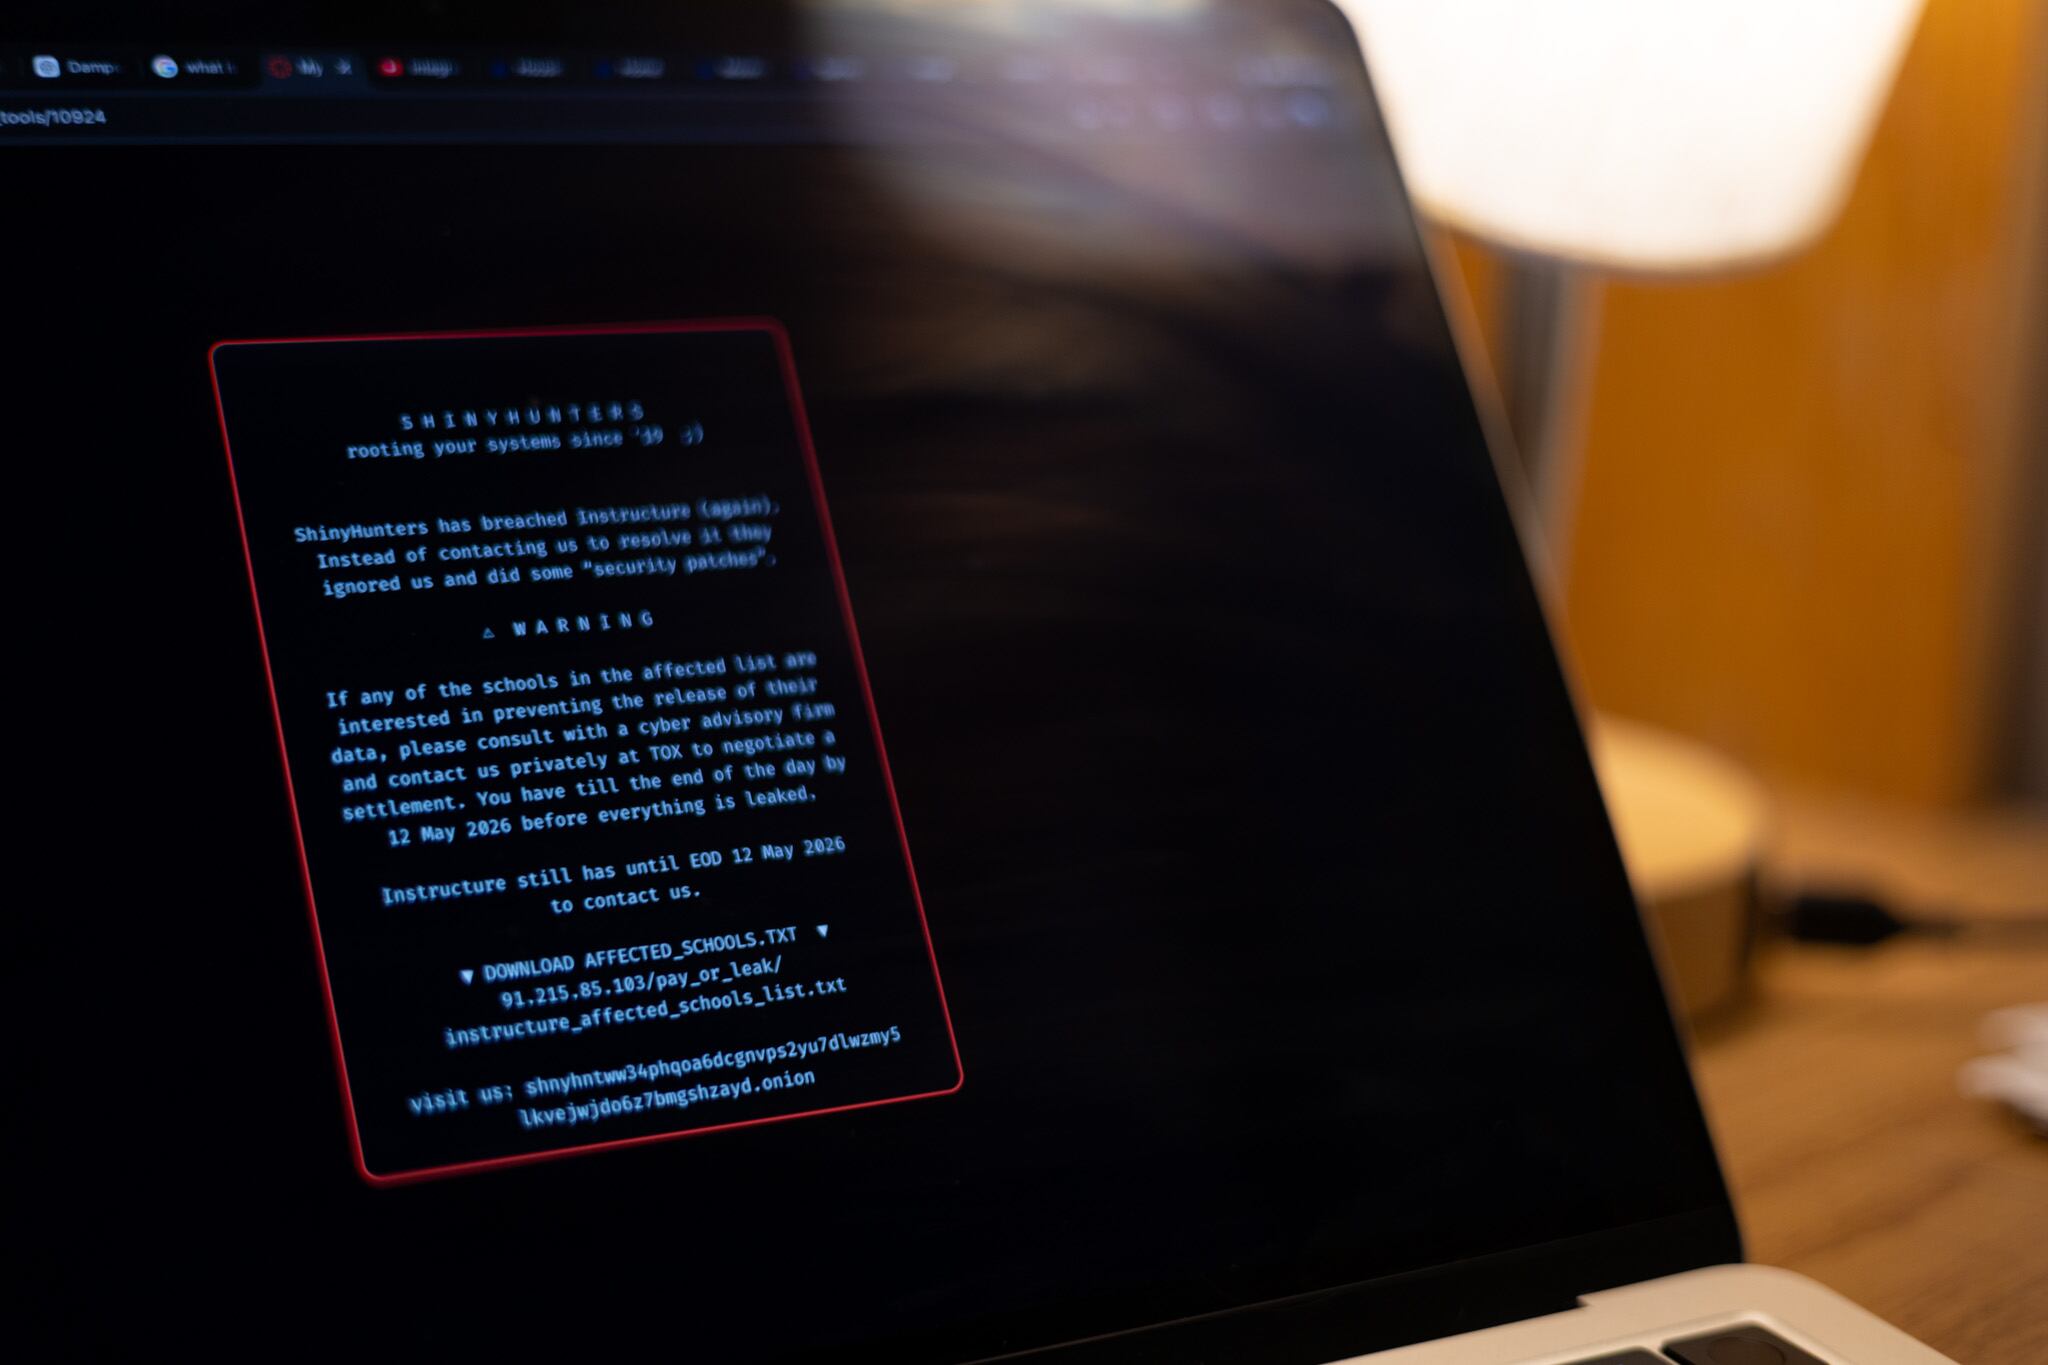
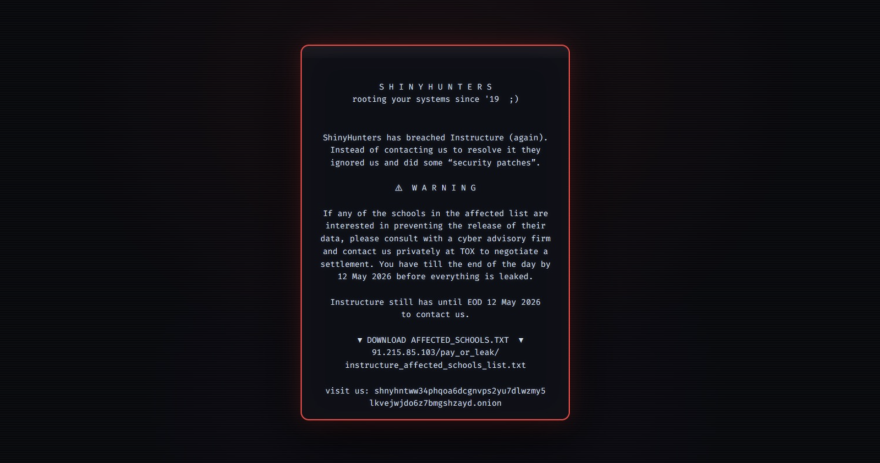
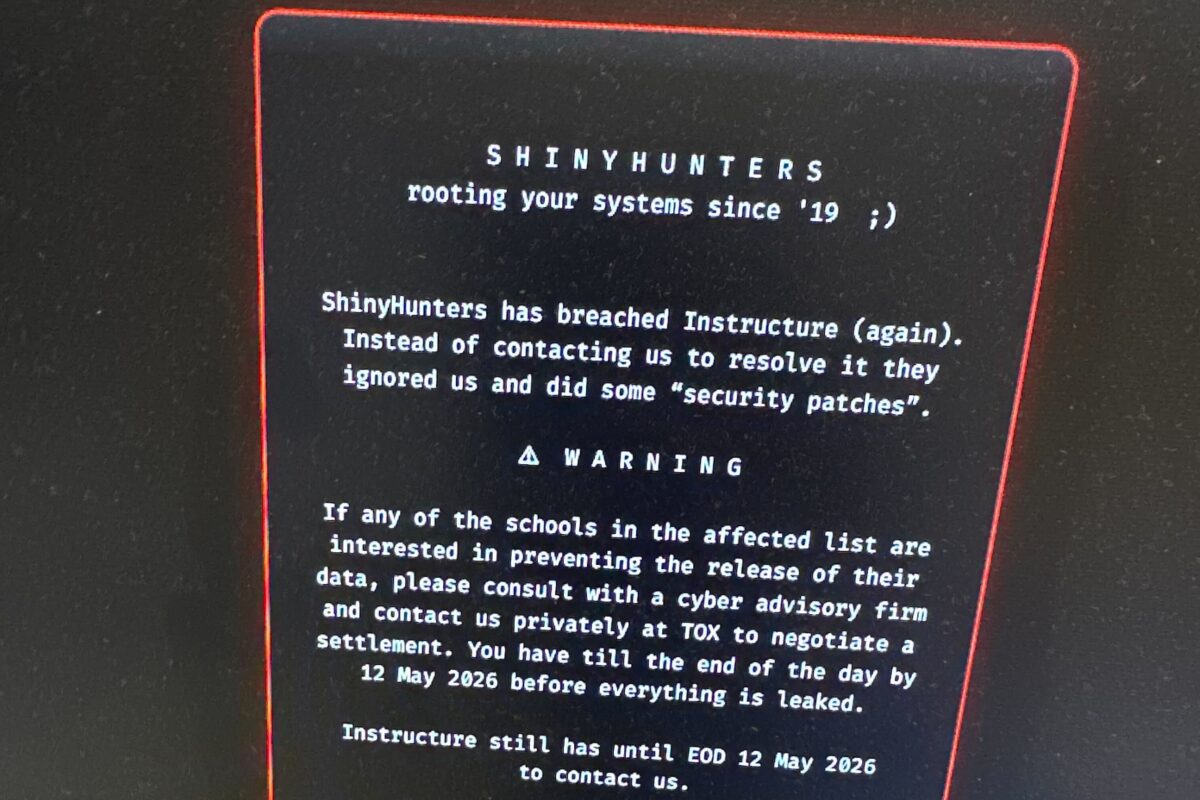
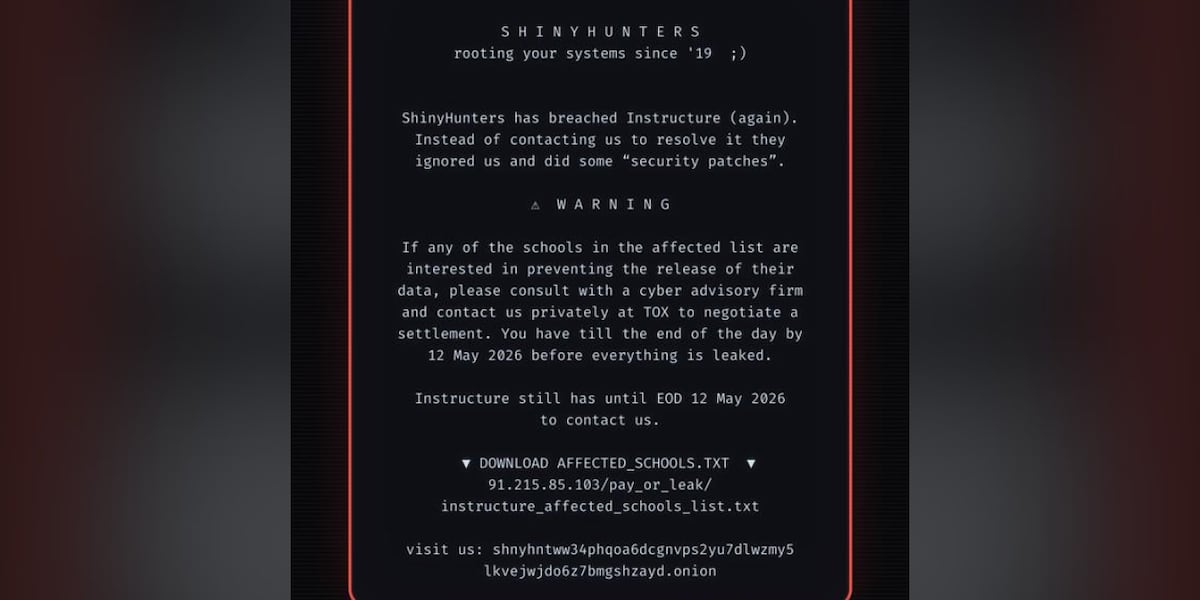
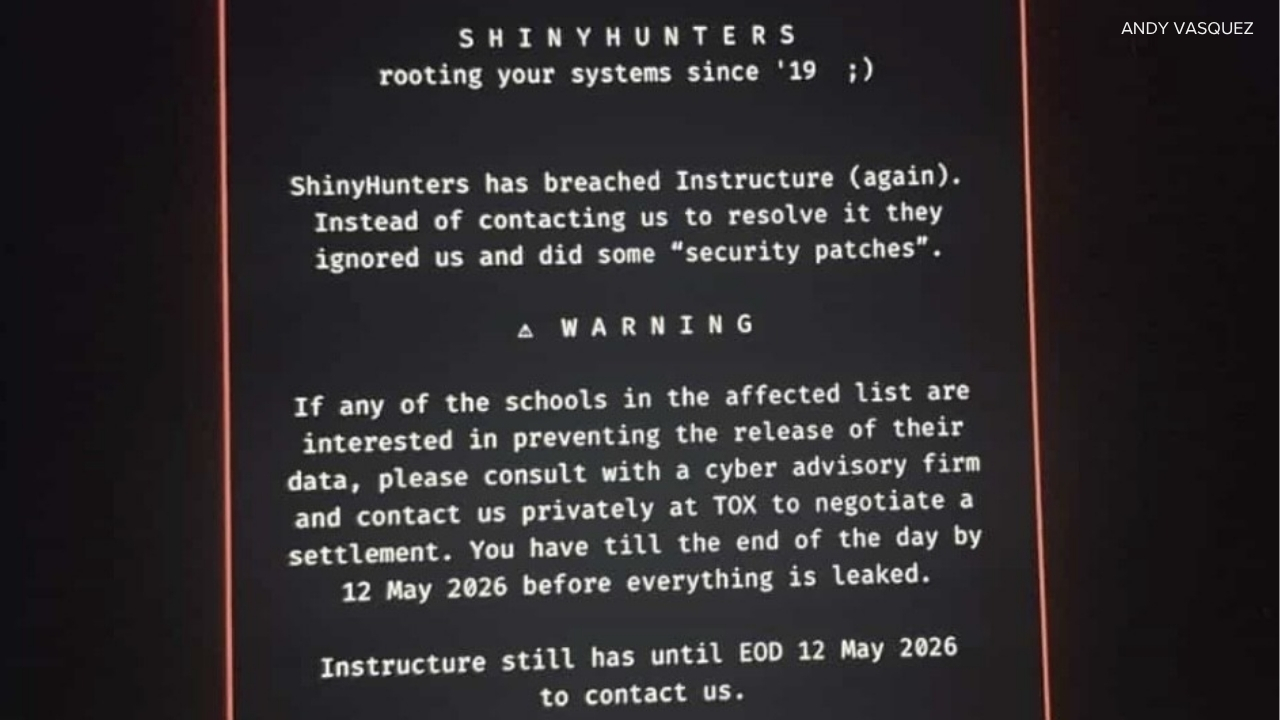
The Canvas LMS cyberattack by ShinyHunters (April 29 and May 8, 2026) disrupted approximately 9,000 educational institutions globally, affecting over 30 million active users during critical finals periods. The attack exploited vulnerabilities in Free-For-Teacher accounts, forcing universities including Penn State, UCLA, University of Toronto, and University of Sydney to cancel or postpone exams. This incident creates a major compliance and certification opportunity for vendors in the educational technology sector.
Regulatory Compliance Implications: The incident has triggered immediate regulatory scrutiny. Senator Chuck Schumer's letter to the Trump administration demanding enhanced cyber defense measures signals incoming federal cybersecurity mandates for educational institutions. Educational institutions managing sensitive student data (names, email addresses, student ID numbers) now face pressure to implement FERPA-compliant security frameworks, SOC 2 Type II certifications, and HIPAA-equivalent data protection standards. Institutions are reassessing security protocols and backup systems, creating demand for compliance consulting services.
Market Elimination & Certification Barriers: Educational software vendors without SOC 2 Type II certification, ISO 27001 compliance, or NIST Cybersecurity Framework alignment will face institutional procurement barriers. Instructure's rapid response—implementing administrative access controls, token management, and enhanced monitoring workflows—sets a new compliance baseline. Vendors lacking these certifications face potential exclusion from institutional contracts worth $500M+ annually in the US education technology market. The fastest compliance path involves third-party audits (60-90 days for SOC 2 Type II, $15,000-40,000 cost) and NIST framework implementation (90-180 days, $20,000-60,000).
Service Gap Opportunities: The incident reveals critical underserved needs: (1) Backup-as-a-Service (BaaS) for educational platforms with 99.99% uptime SLAs, (2) Ransomware response consulting for institutions, (3) Compliance automation tools for FERPA/COPPA/GDPR requirements, and (4) Incident response training for educational IT staff. Institutions are actively seeking alternative platforms and backup solutions, creating a 12-18 month procurement window for compliant vendors. Non-compliant competitors face estimated 40-60% market share loss in institutional contracts as procurement teams implement mandatory security requirements.
Questions 8
What percentage of educational software vendors lack required compliance certifications?
Industry estimates suggest **60-75% of educational software vendors** lack SOC 2 Type II certification or equivalent security standards. The Canvas incident has triggered institutional procurement policies requiring these certifications, effectively creating a **compliance barrier** that eliminates non-compliant competitors. Institutions are implementing mandatory security requirements, forcing vendors to choose between: (1) rapid compliance investment ($45,000-130,000, 6-9 months), (2) market exit. Vendors achieving compliance within 6-9 months can capture 30-50% market share from institutions switching away from non-compliant platforms. The compliance gap represents a **$500M-1B opportunity** for vendors willing to invest in certification and security infrastructure.
How does the Canvas attack create opportunities for backup and disaster recovery vendors?
The Canvas outage forced institutions to cancel finals and lose access to critical course materials, revealing a massive gap in backup infrastructure. Educational institutions are now actively procuring **Backup-as-a-Service (BaaS) solutions** with 99.99% uptime SLAs and geographic redundancy. The market for educational backup solutions is estimated at $200-300M annually, with growth accelerating post-incident. Vendors offering automated backup, rapid recovery (RTO <1 hour), and FERPA-compliant data handling can capture 30-50% market share from institutions upgrading systems. Implementation costs range from $5,000-20,000 per institution, creating a $1.5-3B addressable market across 9,000 affected institutions.