


Windows 11 BitLocker Bypass Crisis | Critical Data Security Risk for E-Commerce Sellers
- YellowKey exploit defeats encryption on millions of devices; GreenPlasma enables privilege escalation; sellers face compliance violations and customer data breach liability







Overview
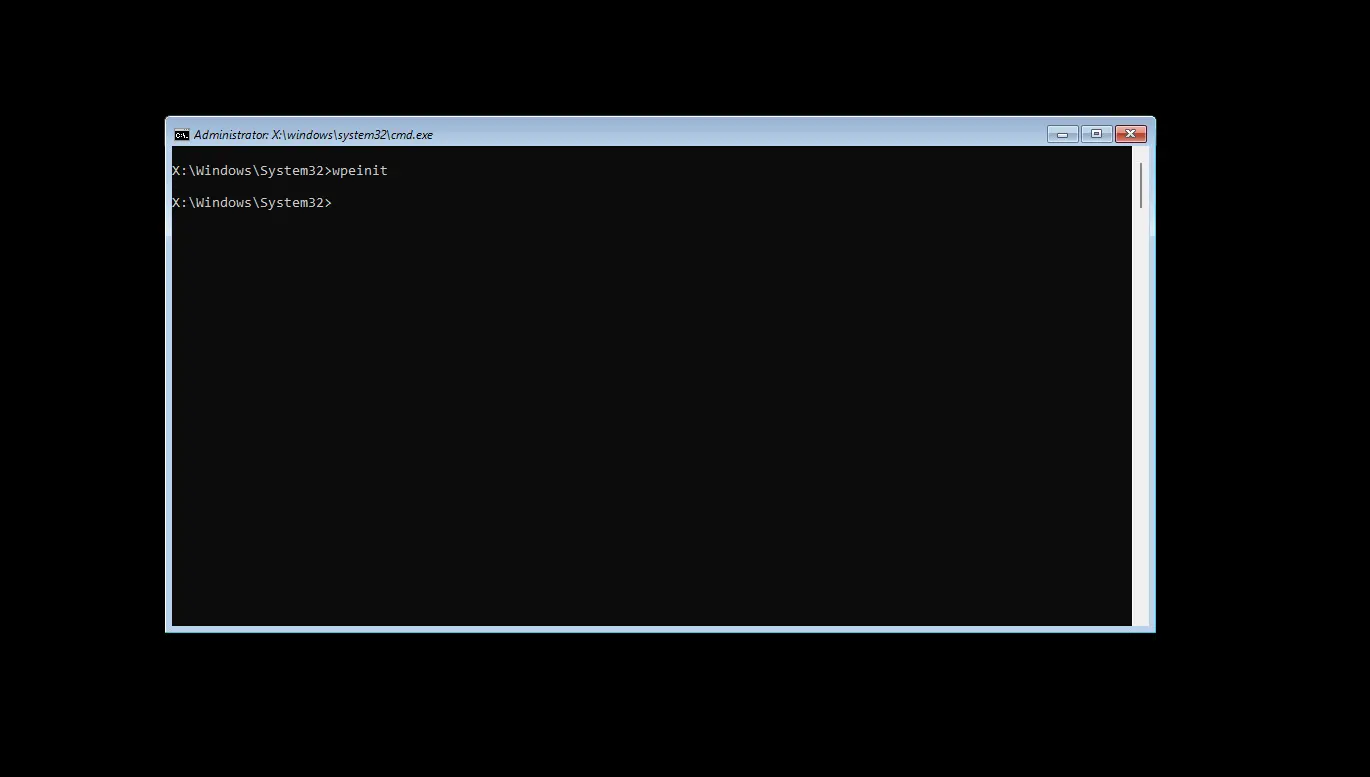
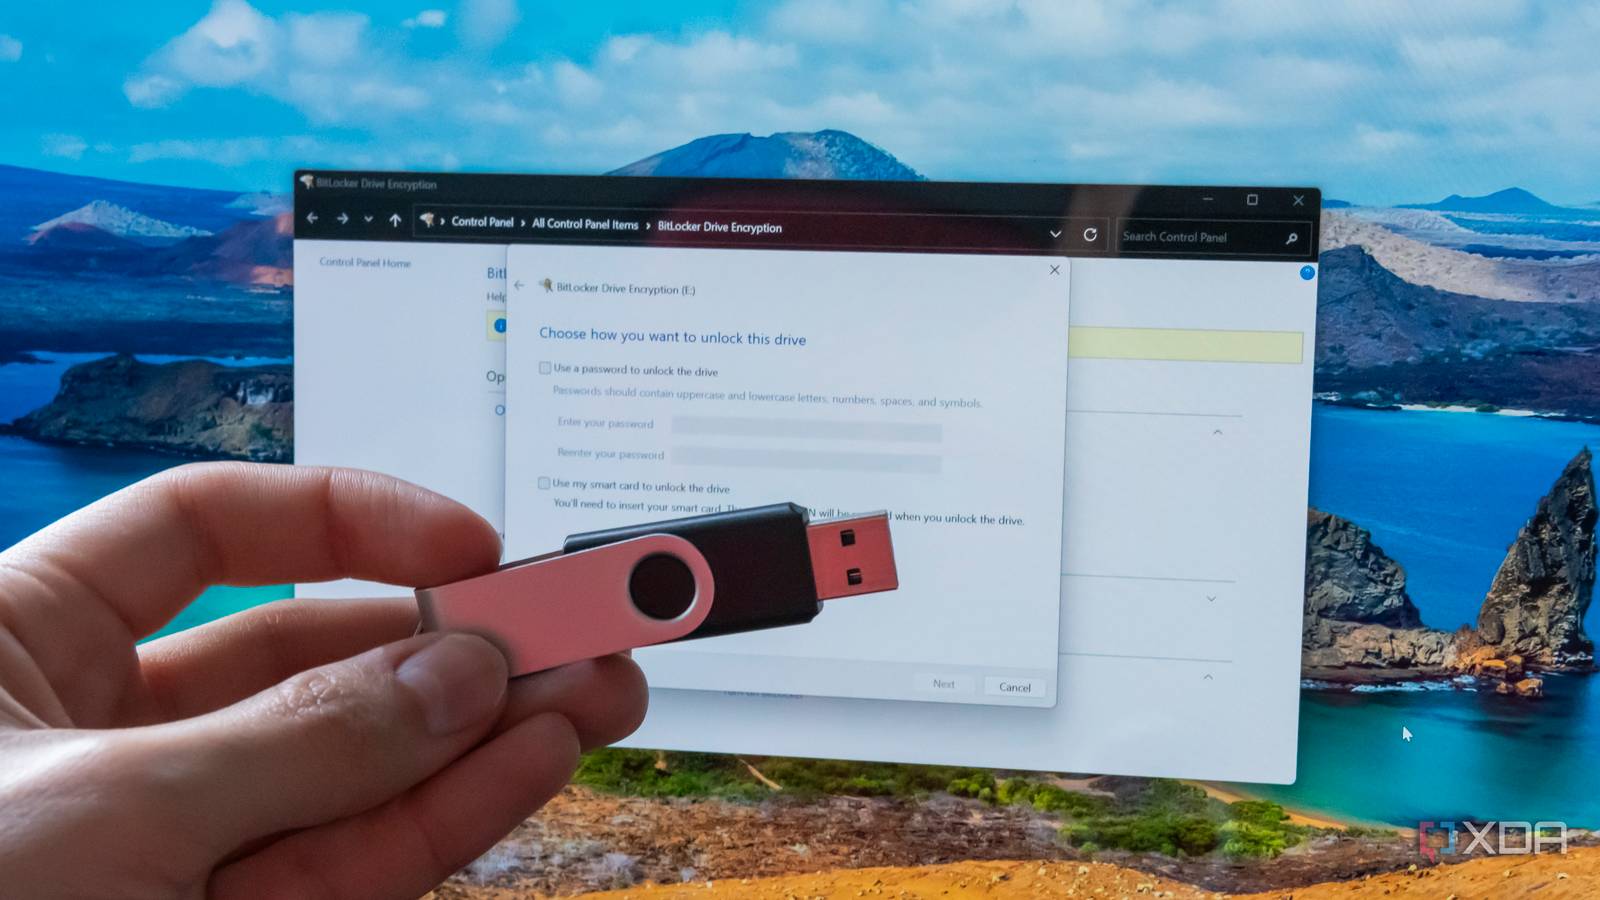
A critical cybersecurity crisis is unfolding that directly threatens cross-border e-commerce operations. Researcher Nightmare-Eclipse disclosed two devastating Windows 11 zero-day vulnerabilities in May 2026: YellowKey (a BitLocker encryption bypass) and GreenPlasma (privilege escalation flaw). YellowKey requires only a USB stick and basic key-holding during system restart to gain unrestricted access to encrypted drives—defeating protections that millions of sellers rely on for customer data protection. The exploit has been independently verified on Windows 11 build 10.0.26100.1 and works against TPM-only mode (the default configuration on most consumer and enterprise machines). GreenPlasma provides SYSTEM-level access for credential harvesting and lateral movement within compromised systems.
For e-commerce sellers, this represents an existential compliance and operational threat. Sellers using Windows 11 devices for inventory management, payment processing, customer database storage, or business operations face immediate risk of data breaches affecting customer payment information, personal data, and intellectual property. The exploit's simplicity—requiring only physical device access and a USB stick—makes it particularly dangerous for sellers with mobile workforces, remote teams, or devices transported across borders. Organizations handling EU customer data face GDPR violation penalties (€20M or 4% of global revenue), while US sellers face FTC enforcement and state data breach notification laws. Sellers operating under government contracts (common in B2B e-commerce) face mandatory encryption requirements that this vulnerability now undermines.
Mitigation options are severely limited. Microsoft has not issued patches or assigned CVE identifiers as of publication. Security experts recommend treating all TPM-only BitLocker devices as unencrypted until patches arrive, requiring strict physical access controls. Switching to TPM-PIN mode is unverified against this exploit. The researcher has promised additional disclosures on the next Patch Tuesday, suggesting more vulnerabilities are forthcoming. Previous disclosures (BlueHammer CVE-2026-32201, RedSun, UnDefend) remain unpatched and are reportedly exploited in real-world attacks according to security firm Huntress. This escalating disclosure campaign, allegedly retaliatory in nature, indicates a pattern of critical Windows vulnerabilities being released without coordinated disclosure timelines.
Immediate seller actions required: Audit all Windows 11 devices storing customer data or payment information; implement additional encryption layers beyond BitLocker (AES-256 third-party solutions); restrict physical access to all devices; consider migrating sensitive operations to non-Windows infrastructure; monitor Microsoft Security Response Center (MSRC) for patch announcements; review cyber liability insurance coverage; prepare customer notification protocols for potential data breaches. Sellers should assume devices are vulnerable until Microsoft releases verified patches.
Questions 8
What is the YellowKey exploit and how does it affect my e-commerce business?
YellowKey is a Windows 11 BitLocker bypass that allows attackers with physical device access to gain unrestricted access to encrypted drives using only a USB stick and basic key-holding during restart. For e-commerce sellers, this means devices storing customer payment data, personal information, or inventory databases can be compromised if physically stolen or accessed. The exploit works against TPM-only mode (default on most machines) and has been independently verified on Windows 11 build 10.0.26100.1. Sellers handling EU customer data face GDPR penalties up to €20M or 4% of global revenue if breached. Immediate action: audit all Windows 11 devices, implement additional encryption layers, and restrict physical access until Microsoft releases patches.
What are the current mitigation options until Microsoft releases patches?
Mitigation options are severely limited. Microsoft has not issued patches or CVE assignments as of publication. Security experts recommend treating all TPM-only BitLocker devices as unencrypted, requiring strict physical access controls. Switching to TPM-PIN mode is unverified against YellowKey. Recommended actions: (1) Implement additional encryption layers beyond BitLocker using third-party AES-256 solutions; (2) Restrict physical access to all devices; (3) Migrate sensitive operations to non-Windows infrastructure if possible; (4) Monitor Microsoft Security Response Center (MSRC) daily for patch announcements; (5) Consider air-gapping critical systems. The researcher promised additional disclosures on the next Patch Tuesday, suggesting more vulnerabilities are forthcoming.