


Meta's Facial Recognition Removal Signals Stricter Biometric Privacy Enforcement | Seller Data Compliance Risk
- Meta removes NameTag facial recognition from 50M+ smart glasses app users; $2.05B in prior settlements establish enforcement precedent for biometric data violations affecting e-commerce seller customer data practices











Overview
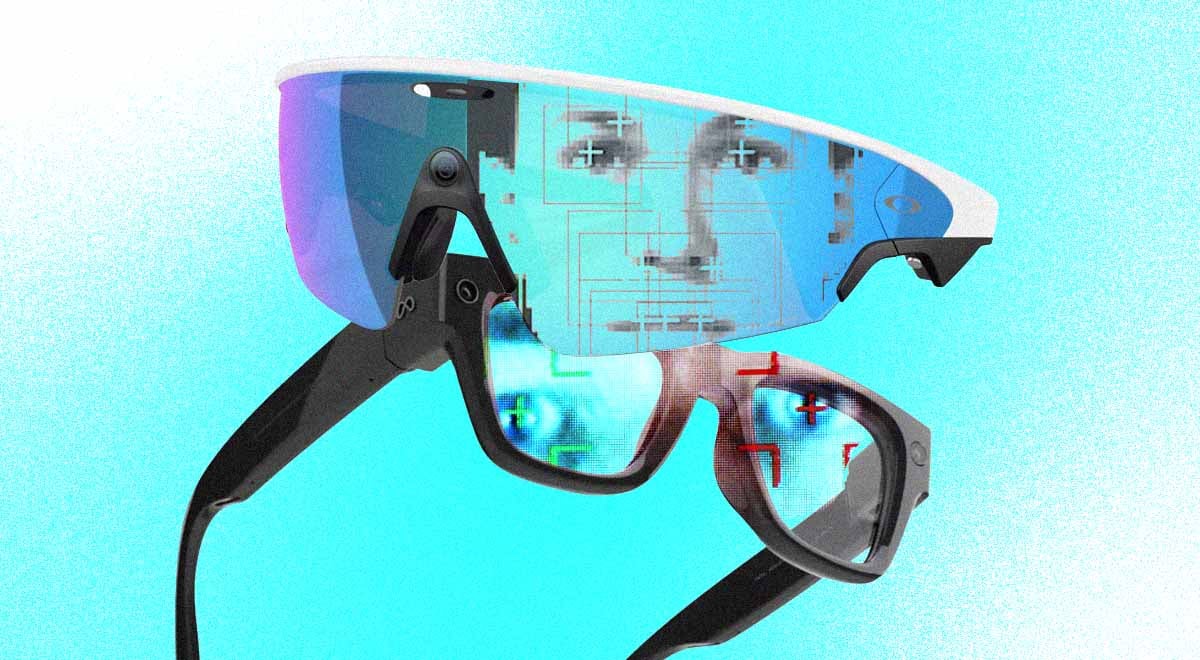
Meta's forced removal of its NameTag facial recognition system from smart glasses apps represents a critical inflection point in biometric privacy enforcement that directly impacts e-commerce sellers relying on Meta's advertising and customer analytics platforms. The company embedded facial recognition code into its Meta AI app (installed on 50+ million phones) to convert faces into 2,048-number biometric signatures called faceprints, discovered June 6, 2024, and completely removed following WIRED's investigation. This incident follows Meta's $1.4 billion Texas settlement (2024) and $650 million federal class action settlement for collecting biometric data without consent—totaling $2.05 billion in enforcement actions that establish regulatory precedent.
The compliance landscape is hardening rapidly across multiple jurisdictions. California's Consumer Privacy Act (CCPA) classifies biometric data as sensitive personal information requiring explicit opt-in consent. Washington, Colorado, and Maryland have enacted comprehensive biometric privacy laws with statutory damages ranging $100-$1,000 per violation. Illinois's Biometric Information Privacy Act (BIPA) carries per-violation penalties that drove Meta's $650M settlement. The Electronic Frontier Foundation confirmed facial recognition code remains embedded in Meta systems, and 70+ civil rights organizations formally urged Meta to abandon facial recognition plans in April 2026, citing stalking and abuse victim risks. Meta's internal memos (reported by New York Times) revealed the company considered launching during periods when "civil society opposition would be distracted"—demonstrating intentional regulatory circumvention that regulators will view as aggravating factor in future enforcement.
For e-commerce sellers, this creates three immediate compliance exposure vectors. First, sellers using Meta's Conversions API, pixel tracking, or audience targeting tools must audit whether customer data flows comply with state biometric privacy laws—particularly if customer photos are processed for lookalike audiences or retargeting. Second, sellers operating in California, Washington, Colorado, Maryland, or Illinois face heightened regulatory scrutiny on any customer data collection practices; non-compliance carries statutory damages of $100-$1,000 per customer per violation. Third, Meta's pattern of embedding undisclosed surveillance features suggests future platform policy changes may retroactively impose compliance obligations on sellers—requiring proactive data governance frameworks. The removal demonstrates that regulatory and public pressure can force rapid platform changes, but only after massive financial penalties and reputational damage. Sellers should expect Meta to implement stricter data handling requirements, potentially including mandatory consent mechanisms for customer analytics and audience targeting—increasing operational complexity for the estimated 8+ million sellers using Meta advertising tools globally.
Questions 8
Which e-commerce product categories face highest biometric privacy compliance risk?
Categories involving customer photos, video, or identity verification face highest risk: (1) Fashion/apparel sellers using virtual try-on or body scanning technology; (2) Beauty sellers using facial recognition for shade matching or skin analysis; (3) Luxury goods sellers using facial recognition for age verification or fraud prevention; (4) Jewelry/watches sellers using facial recognition for authentication; (5) Eyewear sellers (especially smart glasses like Ray-Ban) using facial recognition for fit or prescription verification. These categories should audit compliance within 30 days. Lower-risk categories (electronics, home goods, books) face lower immediate compliance burden but should still implement consent mechanisms for any customer photo collection. Sellers in high-risk categories should consider hiring compliance counsel ($5K-$15K) to audit data practices and implement consent frameworks before regulatory enforcement escalates.
What penalties do sellers face if customer data violates biometric privacy laws?
Statutory damages under state biometric privacy laws range $100-$1,000 per violation per customer. For example, if a seller collects facial recognition data from 10,000 California customers without explicit consent, potential liability is $1M-$10M under CCPA. Illinois BIPA carries similar per-violation damages that drove Meta's $650M settlement. Federal FTC enforcement adds additional penalties: up to $43,792 per violation (2024 civil penalty amount) plus injunctive relief requiring data deletion and compliance monitoring. Class action lawsuits are common—Meta's $650M federal settlement was a class action. Sellers should assume that any biometric data violation will trigger: (1) customer lawsuits within 6-12 months; (2) regulatory investigation within 12-18 months; (3) settlement costs of $500K-$5M+ depending on customer base size. Immediate compliance is significantly cheaper than litigation defense.