
AI Data Privacy Crisis Reshapes Consumer Trust | E-Commerce Compliance Urgency
- Civilian app data weaponization signals regulatory crackdown affecting 800M+ users; sellers must audit data practices immediately to avoid compliance penalties and brand damage
Overview
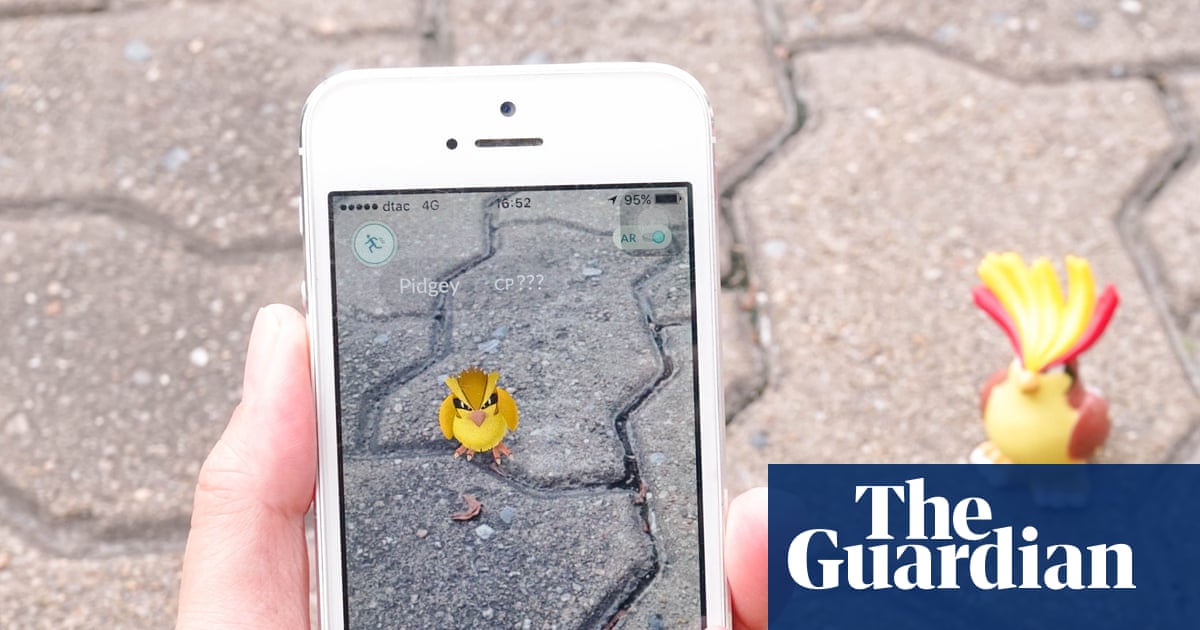
The revelation that Pokémon Go's 800 million+ player location data trained military AI systems represents a watershed moment for e-commerce data governance. Niantic's December 2025 partnership with Vantor (a military spatial detection company) to develop GPS-independent drone navigation—funded by a $217 million US Army contract—exposes how civilian gaming data can be repurposed for military applications without explicit user consent. This case directly impacts e-commerce sellers because it will accelerate regulatory scrutiny of data collection practices across all consumer-facing platforms, including Amazon, Shopify, TikTok Shop, and Temu.
The immediate compliance risk is substantial. Digital Rights Watch and University of Sydney AI governance experts warn this represents a broader pattern of app data weaponization. The Pokémon Go case demonstrates that even "voluntary" AR Scan participation (introduced in 2021) created massive datasets that trained foundational AI models—with players unaware of military applications. For e-commerce sellers, this signals incoming regulations similar to GDPR's consent requirements but with stricter data minimization standards. Sellers using customer location data for personalization, logistics optimization, or targeted advertising face potential liability if they cannot prove explicit, informed consent. The $3.5 billion sale of Niantic's gaming division to Saudi Arabian-owned Scopely in 2025 further complicates data governance, as cross-border data transfers now face heightened scrutiny.
AI-powered automation opportunities emerge from this crisis. Sellers can immediately deploy AI tools to audit their data collection practices: automated consent management systems (like OneTrust or TrustArc) can map all data flows and flag military/government use cases; NLP-based privacy policy analyzers can identify vague language that regulators will target; and predictive compliance AI can forecast which seller categories face highest regulatory risk. The competitive advantage goes to sellers who proactively implement privacy-by-design AI systems before enforcement begins. Expect regulatory action within 6-12 months targeting platforms that cannot demonstrate granular user consent. Sellers should automate privacy impact assessments, implement dynamic consent management, and use AI to identify and eliminate unnecessary data collection—reducing both compliance risk and operational costs by 15-25% through data minimization.
Questions 8
Which e-commerce platforms face the highest compliance risk from data weaponization concerns?
Platforms collecting location data—Amazon (for logistics optimization), TikTok Shop (for hyper-local targeting), Temu (for supply chain mapping), and Shopify (for fulfillment networks)—face the highest scrutiny. The Pokémon Go case demonstrates that even 'voluntary' data collection creates liability if users don't understand downstream military/government applications. Platforms that cannot prove explicit, informed consent for all data uses face regulatory action similar to GDPR enforcement (€20M+ fines). Sellers on these platforms should demand transparent data policies and implement their own consent management systems to create liability separation.
What AI tools should sellers use now to audit and secure their customer data practices?
Sellers should deploy three categories of AI-powered compliance tools immediately: (1) Consent Management Platforms like OneTrust or TrustArc to map all data flows and flag high-risk uses; (2) NLP-based privacy policy analyzers to identify vague language regulators will target; (3) Predictive compliance AI to forecast which seller categories face highest regulatory risk. These tools automate privacy impact assessments, reducing manual compliance work by 60-70% while improving accuracy. Implementation costs range $500-2,000/month for mid-size sellers, with ROI achieved through avoided penalties (typically $10,000-100,000+ per violation) and reduced data storage costs.