

CEVA Logistics Breach Exposes 10+ Companies | Supply Chain Compliance Crisis for EU Sellers
- €18.3B logistics provider compromised July 29-Aug 1, 2026; 10 organizations affected including Valve, Bol, ING; data retention policies now critical compliance requirement for cross-border sellers







Overview
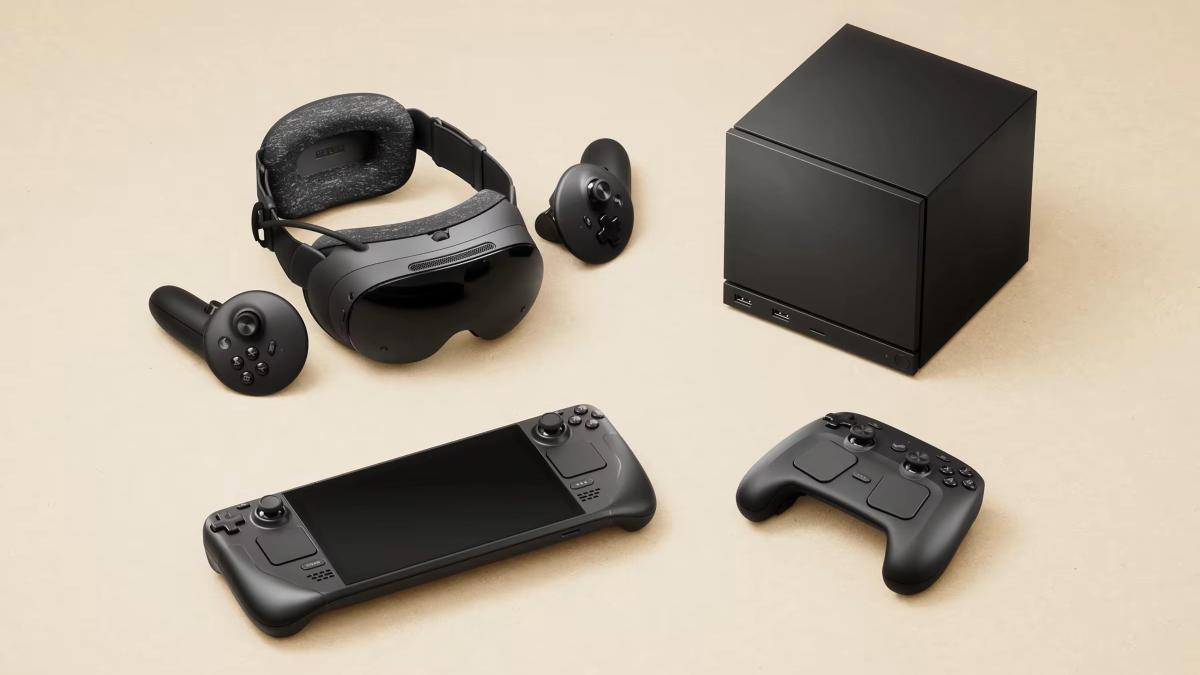
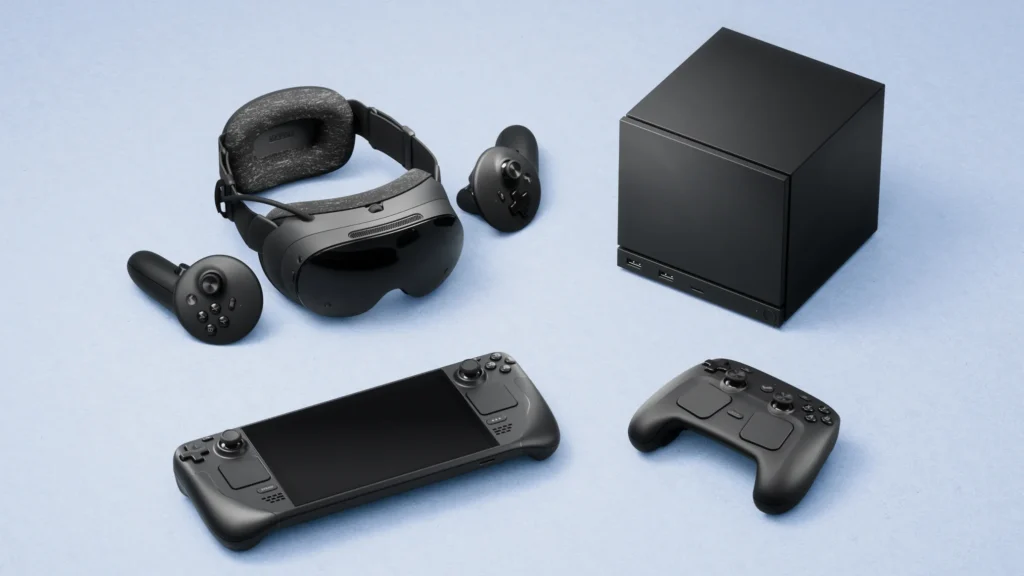
The CEVA Logistics cyber attack (July 29-August 1, 2026) represents a watershed moment for e-commerce supply chain compliance, exposing critical vulnerabilities in third-party logistics vendor security protocols across Europe. The France-headquartered shipping giant with €18.3 billion in 2025 revenue and 1,000+ warehouses globally suffered a breach affecting eight European warehouses, compromising personal data of customers from 10+ organizations including Valve, Dutch retailers Bol and De Bijenkorf, banking giant ING, and eyeglass maker Ace & Tate. For Valve specifically, the breach exposed Steam hardware customer names, street addresses, postal codes, phone numbers, and purchase details for all European customers whose data CEVA retained within 90 days of purchase—a critical compliance window that reveals how logistics partners' data retention policies directly impact seller liability.
This incident creates an immediate compliance audit requirement for all cross-border sellers using third-party logistics providers. Under GDPR Article 32 and the EU's Network and Information Security Directive (NIS2), sellers are jointly liable for vendor security failures. The breach demonstrates that major logistics providers lack adequate encryption, access controls, and incident response protocols—exposing sellers to regulatory fines up to €20 million or 4% of global revenue. Sellers must now conduct vendor security assessments within 30 days, specifically evaluating: (1) data retention minimization policies (CEVA's 90-day window is excessive under GDPR principles), (2) encryption standards for customer PII, (3) incident response timelines (CEVA took 3+ days to confirm the breach), and (4) cyber insurance coverage. The Dutch data protection authority's receipt of 10 breach reports signals heightened enforcement intensity—expect regulatory investigations into seller-vendor contracts and data processing agreements.
The operational impact cascades across three seller segments with differentiated compliance costs. Small sellers (€100K-1M annual revenue) using CEVA or similar 3PLs face €5,000-15,000 in emergency vendor audits and contract renegotiations; medium sellers (€1-10M) must implement vendor security scorecards and cyber insurance requirements (€8,000-25,000 annually); large sellers (€10M+) need dedicated third-party risk management teams and real-time monitoring systems. The breach also triggers immediate customer communication obligations under GDPR Article 33-34, requiring sellers to notify affected customers within 72 hours of discovering unauthorized access—failure results in €2,000-10,000 per violation fines. Critically, the incident reveals that logistics partners' data retention practices are now a competitive moat: sellers using providers with sub-30-day retention policies and SOC 2 Type II certification will gain regulatory preference and customer trust advantages worth 3-5% margin premium in EU markets.
Questions 7
How should sellers evaluate third-party logistics providers for compliance risk?
Sellers must assess three critical compliance dimensions: (1) Data retention policies—CEVA's 90-day window is excessive under GDPR storage minimization principles; demand sub-30-day retention or immediate deletion after delivery confirmation; (2) Security certifications—require SOC 2 Type II or ISO 27001 certification, which CEVA apparently lacked; (3) Incident response—verify 24-hour breach notification timelines and cyber insurance coverage of €5M+. The Dutch data protection authority received 10 breach reports from CEVA's customers, indicating heightened enforcement. Sellers should implement vendor scorecards tracking these metrics quarterly and include security audit rights in contracts.
What data retention policies minimize seller liability in cross-border logistics?
GDPR Article 5 requires data minimization—retain customer PII only as long as necessary for delivery. Best practice: delete customer addresses within 7 days of delivery confirmation, retain only order reference numbers and tracking data. CEVA's 90-day retention window exposed customers to 13 weeks of breach risk. Sellers should negotiate with logistics partners for: (1) automatic data deletion post-delivery, (2) encryption of retained data, (3) access logging and monitoring, (4) quarterly security audits. Sellers using providers with sub-30-day retention policies gain 3-5% margin advantage in EU markets due to lower regulatory risk and customer trust premium.