
Critical Payment Security Breach | Stripe Merchants Face Immediate API Key Exposure Risk
- Stripe merchant API key leak threatens payment processing security for cross-border sellers; immediate credential rotation and multi-factor authentication required to prevent unauthorized access to customer data and transaction records

Overview
The Stripe merchant API key leak represents an immediate and critical compliance threat to cross-border e-commerce sellers, with compromised credentials enabling unauthorized access to payment systems, customer data, and transaction records. This security incident, combined with Apple's unspecified user warnings and Microsoft Copilot vulnerabilities, creates a convergence of payment processor, platform, and AI-assisted system weaknesses that directly impacts seller operational security and regulatory compliance obligations.
For sellers using Stripe as their primary payment processor, the API key exposure creates immediate financial and legal liability. Compromised API credentials allow attackers to access transaction histories, customer payment information, and potentially initiate fraudulent charges or refunds. Sellers must immediately audit API key usage in their Stripe dashboard, rotate all potentially compromised credentials, and implement API key rotation policies (recommended quarterly). The incident underscores that payment processor security is now a compliance requirement—not optional—for sellers handling customer payment data. Under PCI DSS (Payment Card Industry Data Security Standard), sellers are responsible for monitoring API key access and maintaining audit logs. Failure to detect and respond to compromised credentials within 24-48 hours can trigger PCI compliance violations, resulting in fines of $5,000-$100,000 per month and potential payment processor account suspension.
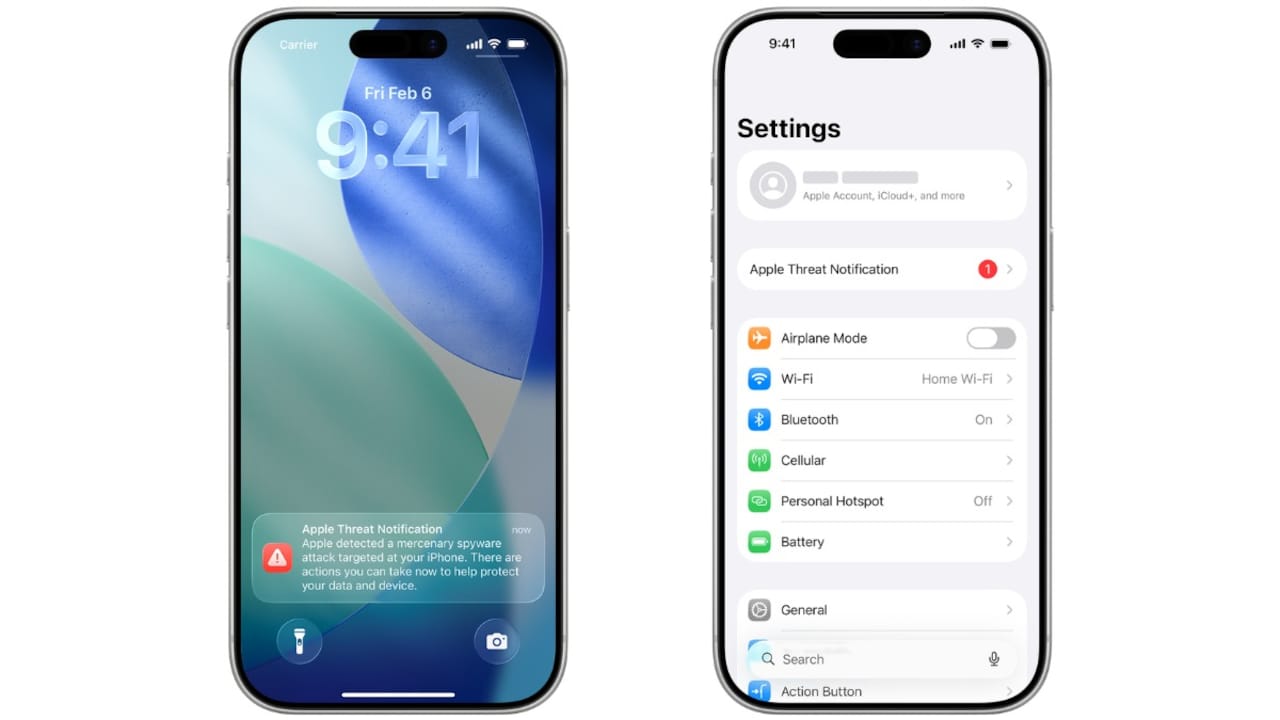
The Apple security warning and Copilot vulnerabilities signal broader platform-level risks for sellers relying on AI tools and iOS/macOS infrastructure. Sellers using Apple devices for business operations, inventory management, or customer service face potential data exposure. More critically, sellers leveraging AI tools like Copilot for product descriptions, customer service automation, or business process optimization now face security risks where AI systems themselves become attack vectors. The Copilot vulnerability demonstrates that AI-assisted business tools can be compromised to expose proprietary business data, customer communications, or operational workflows. This creates a new compliance category: AI tool security vetting. Sellers must now evaluate whether their AI service providers (ChatGPT, Copilot, Claude) have adequate security controls before uploading sensitive business data, customer lists, or product information.
The convergence of these security incidents creates a complex risk environment requiring immediate seller action across three compliance dimensions: payment processor security, platform security, and AI tool governance. Sellers operating on Amazon, Shopify, eBay, or other platforms must now implement multi-factor authentication (MFA) across all payment and business platforms, maintain vigilant monitoring of account access logs, and establish incident response procedures for credential compromise. The estimated timeline for full compliance implementation is 2-4 weeks for small sellers (under 100 SKUs) and 4-8 weeks for larger operations. Non-compliance creates cascading risks: payment processor account suspension (immediate), PCI DSS violations ($5K-$100K/month fines), customer data breach liability (GDPR/CCPA fines up to 4% of revenue), and reputational damage affecting customer trust and repeat purchase rates.
Questions 8
What is the relationship between the Stripe breach and PCI DSS compliance?
PCI DSS (Payment Card Industry Data Security Standard) requires merchants to maintain secure API key management, implement access controls, and monitor for unauthorized access. The Stripe API key leak represents a PCI DSS violation because compromised credentials indicate inadequate key management and access monitoring. Sellers are responsible for detecting and responding to compromised credentials within 24-48 hours. Non-compliance triggers fines of $5,000-$100,000 per month and potential payment processor account suspension. Sellers must implement PCI DSS requirement 2.1 (change default credentials), requirement 8.2 (strong authentication), and requirement 10.2 (audit logging). The incident demonstrates that payment processor security is now a seller compliance obligation, not just the processor's responsibility.
How does the Stripe security breach affect cross-border e-commerce sellers?
Cross-border sellers face heightened compliance risk because they handle customer payment data across multiple jurisdictions (US, EU, Asia Pacific), each with different data protection regulations. The Stripe API key leak creates liability under PCI DSS, GDPR (EU), CCPA (California), and equivalent regulations in other markets. Compromised credentials could expose customer payment information, triggering breach notification requirements and potential fines up to 4% of annual revenue under GDPR. Cross-border sellers must implement enhanced security controls: API key rotation, multi-factor authentication, and audit logging. The incident also signals that payment processor security is now a compliance requirement, not optional, for sellers handling international transactions.