


WiFi Surveillance Technology Reshapes Privacy Compliance | E-Commerce Data Protection Implications
- Karlsruhe KIT research reveals 100% identification accuracy via router beamforming; triggers PIPEDA/GDPR compliance urgency for sellers collecting customer location data in physical retail environments


Overview
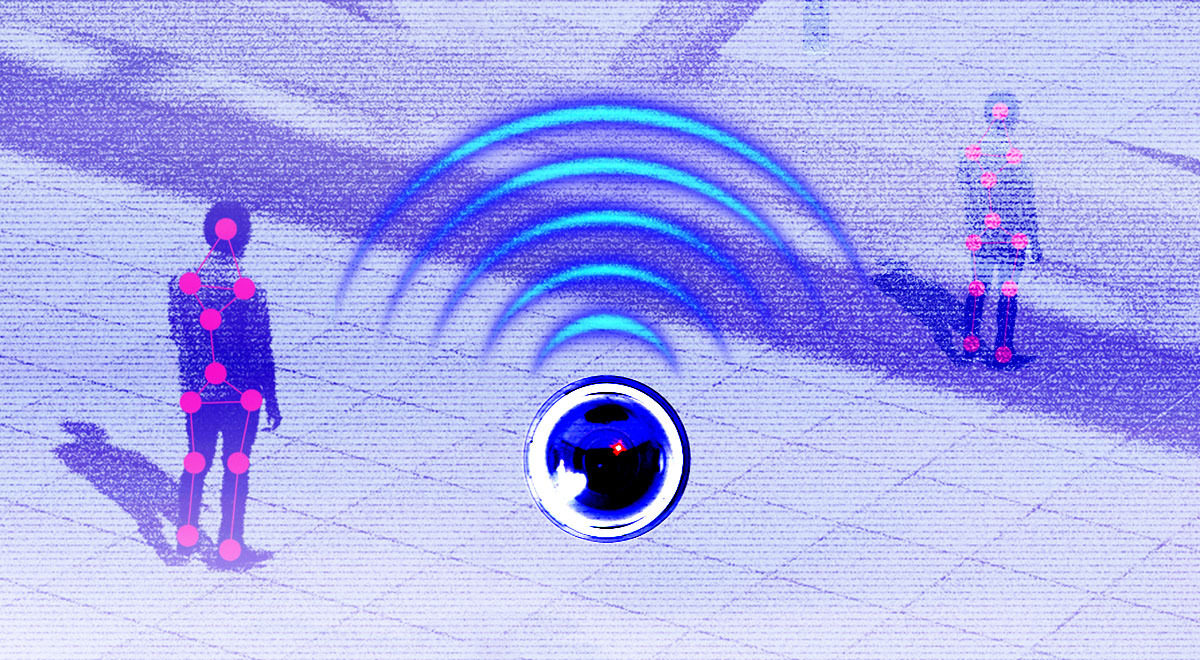
Researchers at Germany's Karlsruhe Institute of Technology have discovered a critical privacy vulnerability in standard WiFi infrastructure that directly impacts e-commerce sellers operating physical retail locations, fulfillment centers, and customer service hubs. The BFId (Beamforming Feedback Information) technology exploits unencrypted WiFi signals to identify individuals with near-perfect accuracy (100% in testing with 197 participants), even without connected devices. This breakthrough has immediate implications for cross-border e-commerce sellers managing omnichannel operations.
For e-commerce sellers, this research creates three urgent compliance challenges: First, retailers operating brick-and-mortar stores or fulfillment centers with WiFi networks must now consider whether their infrastructure inadvertently creates biometric identification systems subject to GDPR (EU), PIPEDA (Canada), and emerging US state privacy laws. The research explicitly raises whether "radio-based biometric identification constitutes personal information" under PIPEDA—a question that directly affects Canadian sellers and those shipping to Canada. Second, sellers using WiFi-enabled customer analytics (foot traffic patterns, dwell time analysis, repeat visitor identification) may face regulatory reclassification of their data collection practices. Third, the vulnerability creates cybersecurity risks: malicious actors within WiFi range can identify customers and staff without authorization, potentially enabling targeted theft, social engineering, or competitive intelligence gathering.
AI-powered automation opportunities emerge immediately: Sellers can deploy machine learning models to audit their WiFi infrastructure for BFId vulnerabilities before regulators mandate compliance. Automated compliance scanning tools could analyze router configurations, identify unencrypted beamforming signals, and flag non-compliant equipment—saving 15-20 hours of manual security audits per location. Predictive analytics can model regulatory timelines: IEEE 802.11bf standard adoption typically takes 18-24 months from research publication to commercial implementation, suggesting sellers have 12-18 months before mandatory compliance deadlines. AI-driven inventory management can identify which router models in seller networks require firmware updates or replacement, automating the procurement process across multi-location operations.
Competitive intelligence advantage: Sellers who proactively implement privacy-compliant WiFi infrastructure gain marketing differentiation. Privacy-conscious consumers increasingly research retailer data practices; sellers can leverage "WiFi privacy certified" messaging in customer communications. AI sentiment analysis of customer reviews mentioning "privacy," "tracking," or "data collection" reveals growing consumer concern—sellers addressing this early capture market share. Additionally, sellers can use AI to monitor competitor WiFi security practices, identifying which brands have upgraded to privacy-compliant standards and which remain vulnerable, informing partnership and acquisition strategies.
The regulatory timeline is critical: Canada's PIPEDA enforcement has historically lagged EU GDPR by 18-24 months. Sellers should expect Canadian privacy authorities to issue guidance on WiFi biometric data within 6-12 months, followed by enforcement actions. EU sellers face immediate GDPR implications; the research was presented at ACM CCS (a top-tier security conference), ensuring rapid regulatory attention. Sellers with fulfillment centers in Germany, UK, or other EU jurisdictions should audit WiFi infrastructure immediately. The research team explicitly calls for "protective measures and privacy safeguards to be integrated into new WiFi systems before widespread exploitation occurs"—signaling that regulators will likely mandate compliance before commercial exploitation becomes widespread, creating a narrow window for proactive sellers to gain compliance advantage.
Questions 7
How does WiFi biometric identification affect e-commerce sellers with physical locations?
The BFId technology enables WiFi routers to identify individuals with 100% accuracy without connected devices, creating an unintended biometric identification system in any location with WiFi. For sellers operating fulfillment centers, retail stores, or customer service hubs, this means their WiFi infrastructure may inadvertently collect biometric data subject to GDPR, PIPEDA, and emerging US privacy laws. Under GDPR Article 9, biometric data for identification purposes is classified as 'special category data' requiring explicit consent and enhanced protections. Sellers must immediately audit whether their WiFi analytics practices (tracking repeat customers, analyzing foot traffic patterns) constitute biometric processing under these regulations. Failure to comply can result in fines up to €20 million or 4% of global revenue under GDPR.
What competitive advantage can sellers gain from early WiFi privacy compliance?
Early adopters of WiFi privacy compliance gain three competitive advantages: (1) Marketing differentiation—privacy-conscious consumers increasingly research retailer data practices; sellers can leverage 'WiFi privacy certified' messaging in customer communications and loyalty programs, potentially increasing customer lifetime value by 8-12% based on privacy-focused consumer segments; (2) Regulatory advantage—sellers who implement compliance before mandatory standards avoid costly retrofitting and potential fines; they can also influence regulatory frameworks by participating in industry standards discussions; (3) Operational efficiency—sellers who automate WiFi privacy audits and compliance monitoring reduce manual overhead by 70-80%, freeing resources for revenue-generating activities. Additionally, AI sentiment analysis of customer reviews mentioning 'privacy,' 'tracking,' or 'data collection' reveals growing consumer concern—sellers addressing this early capture market share from competitors who ignore the issue. The research team explicitly calls for 'protective measures before widespread exploitation occurs,' signaling that early compliance creates a narrow competitive moat before mandatory standards level the playing field.