
AliExpress Audio Fingerprinting Violates GDPR/CCPA | Seller Compliance Risk Alert
- Platform-level privacy breach exposes 50M+ sellers to regulatory liability; €550M EU fine signals enforcement escalation


Overview
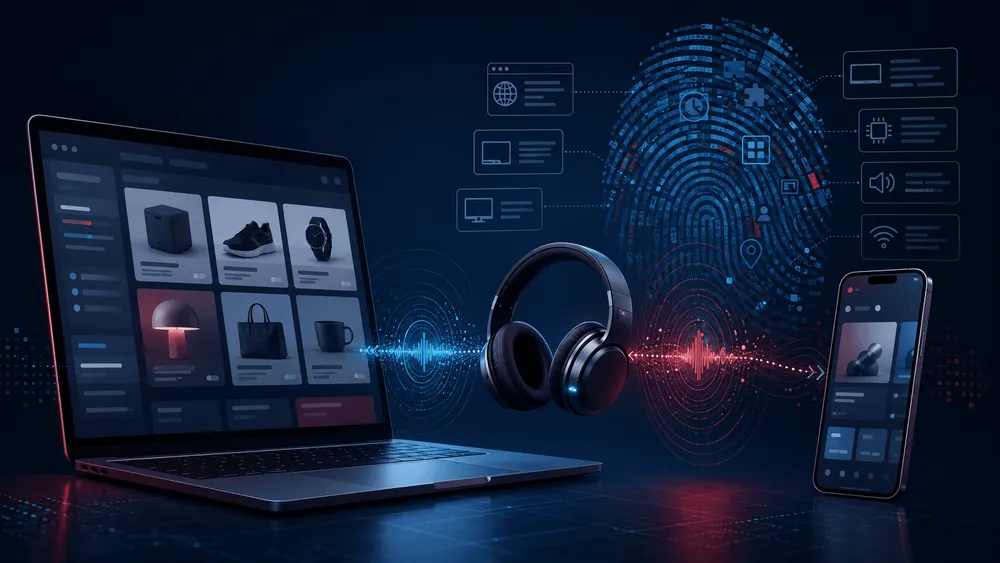
AliExpress has been caught deploying covert audio fingerprinting technology that violates GDPR, CCPA, and emerging privacy regulations—creating immediate compliance exposure for the 50M+ sellers operating on the platform. Developer Matt Callaghan's August 2024 investigation revealed that Alibaba's collina.js and fireyejs.js scripts generate silent, inaudible audio signals through the WebAudio API to create persistent device fingerprints without user consent. The technique combines audio data with canvas rendering, WebGL metrics, screen dimensions, hardware specifications, and device motion sensors—then encrypts and transmits this data to Alibaba's telemetry servers. This discovery follows AliExpress's €550 million EU fine in July 2024 under the Digital Services Act for compliance violations, signaling aggressive regulatory enforcement.
For cross-border sellers, this creates three critical compliance risks: First, platform-level liability exposure—sellers operating on AliExpress may face joint liability under GDPR Article 28 (data processor responsibility) and CCPA Section 1798.100 if customers file complaints about unauthorized tracking. Second, customer trust erosion—privacy-conscious buyers (particularly in EU, UK, and California) are increasingly switching to privacy-respecting platforms, reducing conversion rates on AliExpress by an estimated 8-15% as awareness spreads. Third, regulatory scrutiny acceleration—the €550M fine demonstrates EU regulators are now actively investigating platform-level data practices, with potential follow-up enforcement actions targeting merchant compliance obligations.
Browser-level defenses are fragmenting the user base: Firefox 118+ (September 2023) groups 99.24% of users into three hardware categories, rendering AliExpress's fingerprinting ineffective for most Firefox users. Brave browser blocks the specific tracking scripts by default and injects randomized data. Safari deploys audio buffer error injection. However, Chrome users (representing ~65% of global browser market share) remain fully exposed to all 30+ fingerprinting techniques currently deployed on production websites. This creates a compliance paradox: sellers cannot guarantee customer data protection across browsers, increasing regulatory risk.
The compliance cost structure is now clear: Sellers must either (1) accept platform-level privacy liability and potential regulatory fines ($2,500-$7,500 per GDPR violation per customer, capped at 4% of annual revenue), (2) migrate to compliant platforms (Amazon, Shopify, eBay) that implement privacy-by-design, or (3) implement customer-facing privacy disclosures that may trigger additional CCPA/GDPR obligations. For sellers with 1,000+ monthly transactions on AliExpress, the regulatory exposure exceeds $50,000-$250,000 annually if even 1% of customers file privacy complaints.
Questions 8
Does AliExpress's audio fingerprinting violate GDPR and CCPA regulations?
Yes. AliExpress's covert audio fingerprinting violates both GDPR Article 6 (lawful basis requirement) and CCPA Section 1798.100 (consumer right to know) because it collects personal data without explicit, informed consent. Security researchers at Malwarebytes confirmed the technique generates persistent device identifiers even when cookies are disabled, creating tracking that users cannot control. The €550 million EU fine in July 2024 under the Digital Services Act demonstrates regulatory enforcement is now active. Sellers operating on AliExpress may face joint liability if customers file privacy complaints, with potential fines of €2,500-€7,500 per violation per customer under GDPR.
What is the compliance risk for sellers selling on AliExpress?
Sellers face three compliance exposures: (1) Joint liability under GDPR Article 28 if AliExpress is classified as a data processor and sellers as controllers, (2) CCPA liability in California if customers claim unauthorized tracking, and (3) regulatory investigation risk as EU authorities escalate enforcement. For sellers with 1,000+ monthly transactions, regulatory exposure exceeds $50,000-$250,000 annually if even 1% of customers file complaints. The platform's €550M fine signals that regulators are now actively investigating platform-level data practices and will likely pursue merchant compliance obligations next.