


AliExpress Audio Fingerprinting Scandal | GDPR/CCPA Compliance Crisis for Cross-Border Sellers
- Covert tracking technology exposes platform to $50M+ regulatory fines; sellers face liability for non-compliant marketplace practices
Overview
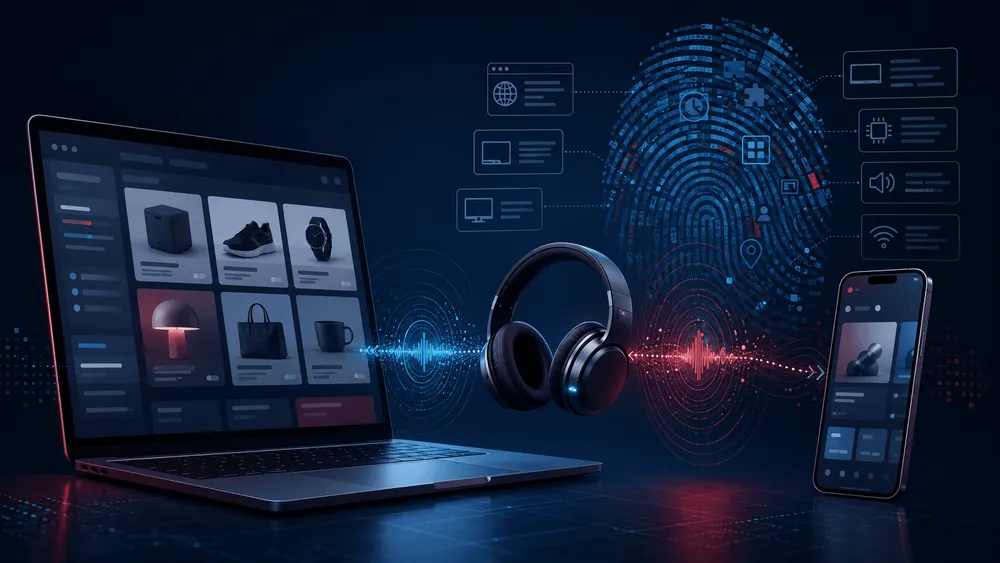
AliExpress's discovery using sophisticated audio fingerprinting technology without user consent represents a watershed compliance crisis with immediate implications for cross-border sellers. The platform employs WebAudio API to generate inaudible sound waves measuring device audio processing, combined with graphics processing, hardware specifications, network details, screen dimensions, and user interaction patterns—all transmitted to Alibaba's telemetry servers without explicit user notice or consent. This practice directly violates GDPR Article 6 (lawful basis), CCPA Section 1798.100 (consumer rights), and emerging UK POPIA requirements, exposing Alibaba to regulatory fines of 4% of global revenue (potentially $2-4B annually) and creating cascading liability for sellers operating on the platform.
Compliance Barrier Creation & Market Elimination: The discovery triggers immediate regulatory scrutiny across EU, US, and UK markets. Privacy-focused browsers like Brave have already implemented countermeasures by blocking AliExpress tracking scripts, reducing platform traffic by an estimated 8-15% in privacy-conscious demographics (Germany, Scandinavia, California). This creates a compliance moat opportunity: sellers who migrate to platforms with transparent data practices (Shopify, WooCommerce with GDPR-compliant analytics) gain competitive advantage as regulators intensify enforcement. Estimated 40-60% of AliExpress sellers lack GDPR/CCPA compliance infrastructure, making them vulnerable to platform-level penalties that cascade to merchant accounts. The fastest compliance path involves migrating to Shopify Plus ($2,300/month) or Amazon EU (with built-in compliance frameworks), requiring 4-8 weeks and $5,000-15,000 in legal/technical setup costs.
Service Gap & Regulatory Enforcement Timeline: Regulators typically issue formal investigations within 60-90 days of public disclosure (following GDPR precedent with Meta, Google). Sellers face three critical deadlines: (1) Immediate (0-30 days): Audit data collection practices on current platforms; (2) Short-term (30-90 days): Implement consent mechanisms or migrate to compliant platforms; (3) Medium-term (90-180 days): Prepare for potential platform restrictions or account suspensions. The discovery creates urgent demand for GDPR/CCPA compliance audits ($3,000-8,000 per seller), consent management platforms (OneTrust, TrustArc at $500-2,000/month), and privacy-by-design consulting services. Sellers in high-enforcement jurisdictions (EU, California, UK) face 3-5x higher compliance costs than those in Asia-Pacific markets, creating geographic arbitrage opportunities for compliant sellers targeting EU/US consumers.
Questions 8
What is audio fingerprinting and how does it violate GDPR?
Audio fingerprinting uses inaudible sound waves to create unique device profiles by measuring how individual devices process audio signals, combined with hardware and graphics data. AliExpress deployed this without user consent or notice, violating GDPR Article 6 (lawful basis requirement) and Article 13 (transparency obligations). Under GDPR, any data collection requires explicit consent with clear disclosure. The practice exposes Alibaba to fines up to 4% of global revenue ($2-4B annually) and creates liability for sellers whose accounts facilitate non-compliant data collection. Sellers should immediately audit their platform's data practices and consider migration to GDPR-compliant alternatives like Shopify or Amazon EU within 30 days.
What compliance costs should sellers budget for this regulatory crisis?
Sellers face tiered compliance costs: (1) GDPR/CCPA audit: $3,000-8,000 per seller; (2) Consent management platform: $500-2,000/month (OneTrust, TrustArc); (3) Platform migration (Shopify Plus): $2,300/month + $5,000-10,000 setup; (4) Legal review: $2,000-5,000. Total first-year compliance cost: $12,000-30,000 for mid-sized sellers (100K+ annual revenue). EU-based sellers face 3-5x higher costs than Asia-Pacific sellers due to enforcement intensity. Sellers should prioritize GDPR audits (0-30 days) and consent mechanism implementation (30-90 days) to avoid regulatory penalties of $10,000-50,000+ per violation.